


On this page
An AI guardrails platform checks every AI input and output against policy before it reaches a model or a person, then blocks, masks, or reroutes whatever breaks the rules.
AI Guardian applies identity, PII masking, policy, model routing, spend caps, and audit trails to every AI request, so teams can use approved AI in Teams, Slack, and web with less shadow AI exposure.
What is an AI guardrails platform?
Definition: An AI guardrails platform is software that enforces policy on AI traffic at runtime. It inspects prompts, files, and responses as they move, applies rules for data, security, topic, access, and cost, and records what it decided.
A platform differs from a single guardrail because it manages many guardrails across users, models, and agents from one place. The term overlaps with three neighbors, and the differences decide what you buy.
| Term | What it does | Where it stops |
|---|---|---|
| AI guardrails | Enforce rules on each request and response at runtime | Needs policy decisions from elsewhere |
| AI governance | Decides policy, ownership, and oversight | Governance platforms may focus primarily on policy, inventory, and oversight rather than inline enforcement |
| AI gateway | Routes traffic to models, and many now add guardrails, identity, budgets, and agent controls | Often built for developer traffic, so employee workspaces and executive reporting vary by product |
| Content filters | Block listed words or harm categories | Do not understand roles, files, or business context |
Governance writes the rules, a gateway moves the traffic, and guardrails enforce the rules on that traffic. A platform that combines all three reduces the gaps between them.
Seven types of enterprise AI guardrails to evaluate
Seven types cover most enterprise risk. Not every product needs to own every layer, and products rarely cover all seven, so use the table to mark which gaps you would fill another way.
| Type | What it checks | Example control |
|---|---|---|
| Input guardrails | Prompts and retrieved content | Prompt injection and jailbreak detection |
| Data guardrails | Text and attached files | PII, secret, and document redaction |
| Output guardrails | Model responses | Toxicity, leaked secrets, and grounding checks |
| Topical guardrails | Subject of the request | Off-domain request blocking |
| Access guardrails | Who may use which model | SSO, role-based access, model permissions |
| Cost guardrails | Usage and spend | Token quotas and department caps |
| Agent guardrails | Tools and actions | Tool allowlists and approval gates |
AI Guardian's controls center on identity, inspection of prompts and files, policy, routing, and audit. The comparison below shows how each approach to guardrails covers these types.
Why do teams need an AI guardrails platform now?
IBM and Cyberhaven both describe risk that comes from how people use models, not from model flaws. IBM's 2026 Cost of a Data Breach Report puts the global average breach cost at $4.99M and reports a 56% increase in AI-driven attacks. Four exposures show up first.
- Shadow AI exposure: IBM's 2026 report found that 68% of breached organizations lacked AI governance policies to manage AI or detect shadow AI, and that security incidents involving shadow AI rose from 20% to 43%.
- Sensitive data leakage: Cyberhaven's 2025 report found that 34.8% of corporate data employees put into AI tools is sensitive, up from 10.7% two years earlier.
- Prompt injection: OWASP ranks it first in its 2025 Top 10 for LLM applications. A retrieved document can carry a hidden instruction the user never sees.
- Missing audit evidence: IBM's 2026 report also found that 92% of organizations with an AI-related breach lacked proper AI access controls. Shared API keys show that a call happened, not who made it.
Find out where shadow AI is already leaking data
Most teams discover unapproved AI use only after sensitive files reach a public model. Running a few sample prompts through a governed path shows where employees use AI today and which guardrails close the biggest gaps first.
Where should AI guardrails be enforced?
IMAGE_URL_HERE in this block's data-image-url attribute with your final image link.
IMAGE_URL_HERE
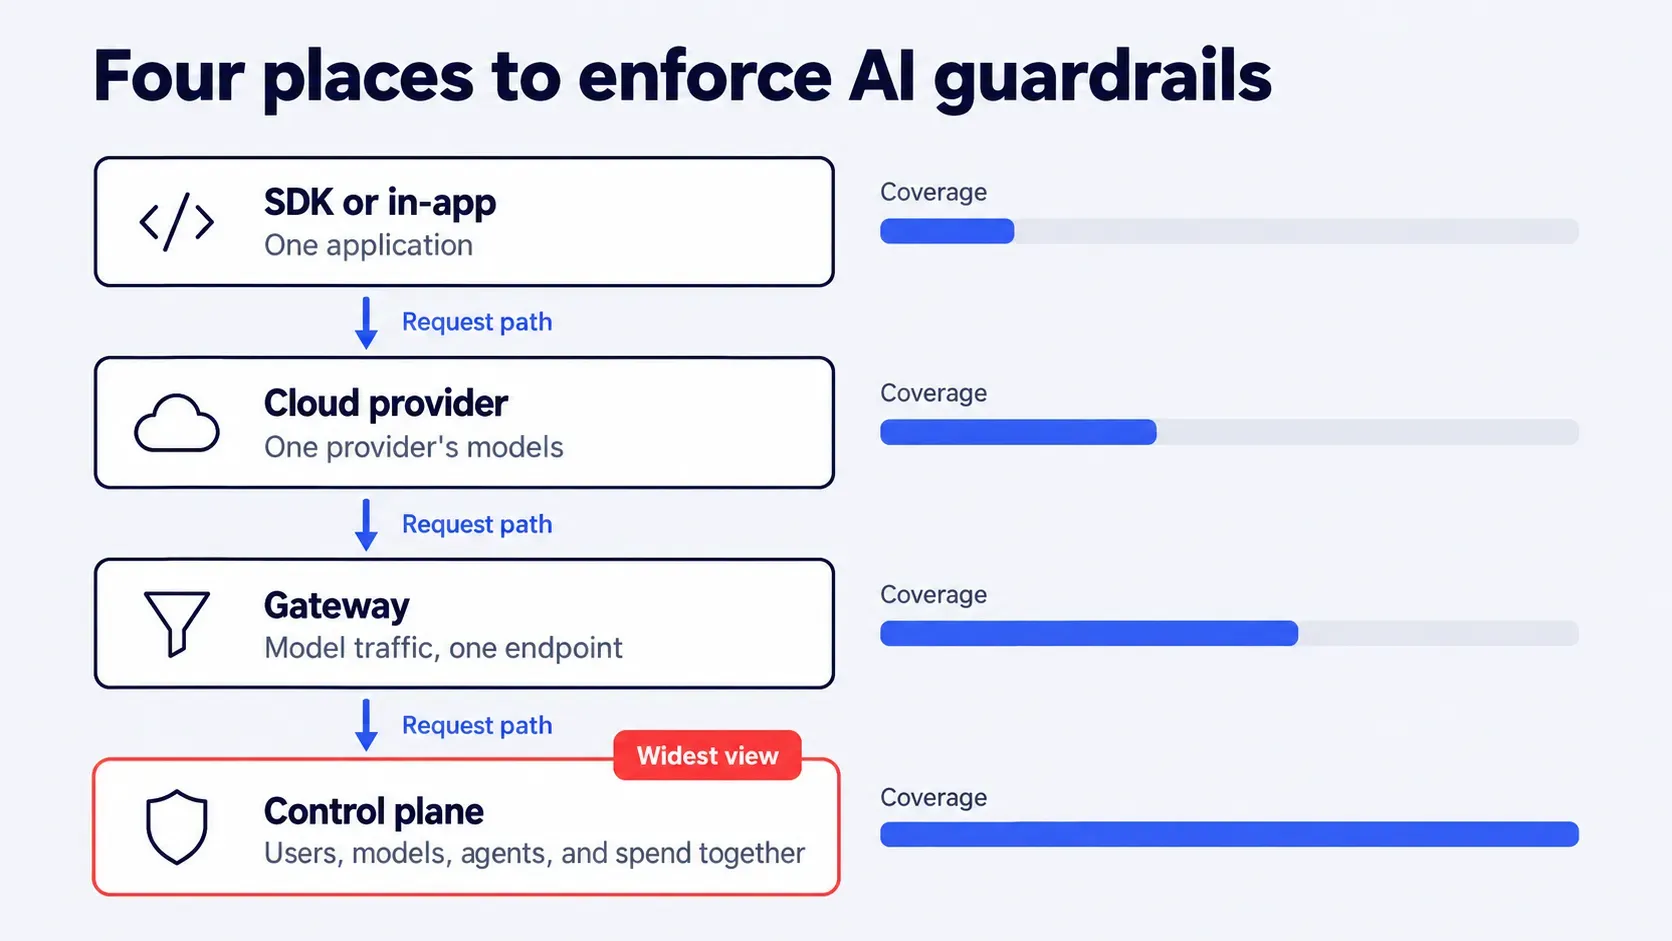
Guardrails can run in four places, and the place decides what they can see. Most teams end up with more than one layer.
| Layer | Scope | Effort | What it cannot see |
|---|---|---|---|
| SDK or in-app | One application | Per-app integration and upkeep | Other apps, employee tools, personal accounts |
| Cloud provider | One provider's models | Low inside that cloud | Other providers and tools outside the cloud |
| Gateway | Model traffic through one endpoint | Moderate | Employee workspaces and who is using what, unless identity is added |
| Control plane | Users, models, agents, and spend together | One deployment | Application internals, so keep app-level tests |
Per-application guardrails work well for the application you ship. They say nothing about the analyst pasting a contract into a personal chatbot account. Cloud-native guardrails stay inside one cloud and one model family.
An enterprise LLM gateway sees every model call but not the person behind it unless identity is attached. A control plane sits where users, models, agents, and budgets meet, so one policy covers all of them.
Expert insight
“A rule written in a policy document does not sit in the request path. A control that runs on every request does, and it only holds if the approved route is also the fastest one.”
AI Guardian is a control plane. It does not replace application-level testing, so teams that ship their own LLM apps usually keep an in-app layer as well.
How to choose an AI guardrails platform: 10 criteria
Agree on who uses the tool and what must stay protected before you compare features. Then test each criterion against your own files, not a vendor demo set.
| # | Criterion | What to verify | Who asks |
|---|---|---|---|
| 1 | Coverage depth and custom policies | Input, output, data, topic, and agent guardrails; rules you can write yourself | CISO, platform engineering |
| 2 | Document-level PII redaction | Multi-page files and regional identifiers, not only pasted text | CISO, compliance |
| 3 | Employee workspace support | Teams, Slack, web, and mobile, so the governed path is convenient | COO, line-of-business heads |
| 4 | Model-agnostic routing | Commercial and custom models, with fallback | Platform engineering |
| 5 | Role-based cost controls | Quotas and caps by role and department, enforced at request time | CIO, CFO |
| 6 | Agent governance | Internal and third-party agents inherit identity and limits | CISO, platform engineering |
| 7 | Private cloud deployment | Runs in your tenant; what leaves it, and where | CISO, compliance |
| 8 | Audit evidence and export | Identity on every record; export to your SIEM or observability tools | CISO, compliance |
| 9 | Latency and false positives | Measured on your traffic; fail open or fail closed when inspection breaks | Platform engineering |
| 10 | Time to value and total cost | Days to deploy; license, hosting, and engineering time | CIO, CFO |
Build, buy, or use open source?
Four routes exist. Engineering capacity and governance depth decide between them, and cost varies with scope, so the comparison is qualitative.
| Factor | Open-source framework | Cloud-native guardrails | Point security tool | Control plane platform |
|---|---|---|---|---|
| Time to deploy | Fast start, slow operations | Fast inside one cloud | Fast for one use case | Days after alignment |
| Coverage | Flexible, you assemble it | One provider's models | Narrow, such as injection | Users, models, agents |
| Ownership | You run and update it | Provider runs it | Vendor runs it | Vendor builds it, runs in your tenant |
| Cost predictability | Engineers and hosting | Usage-based | License | Setup plus license |
How to test a platform in a demo
IMAGE_URL_HERE in this block's data-image-url attribute with your final image link.
IMAGE_URL_HERE
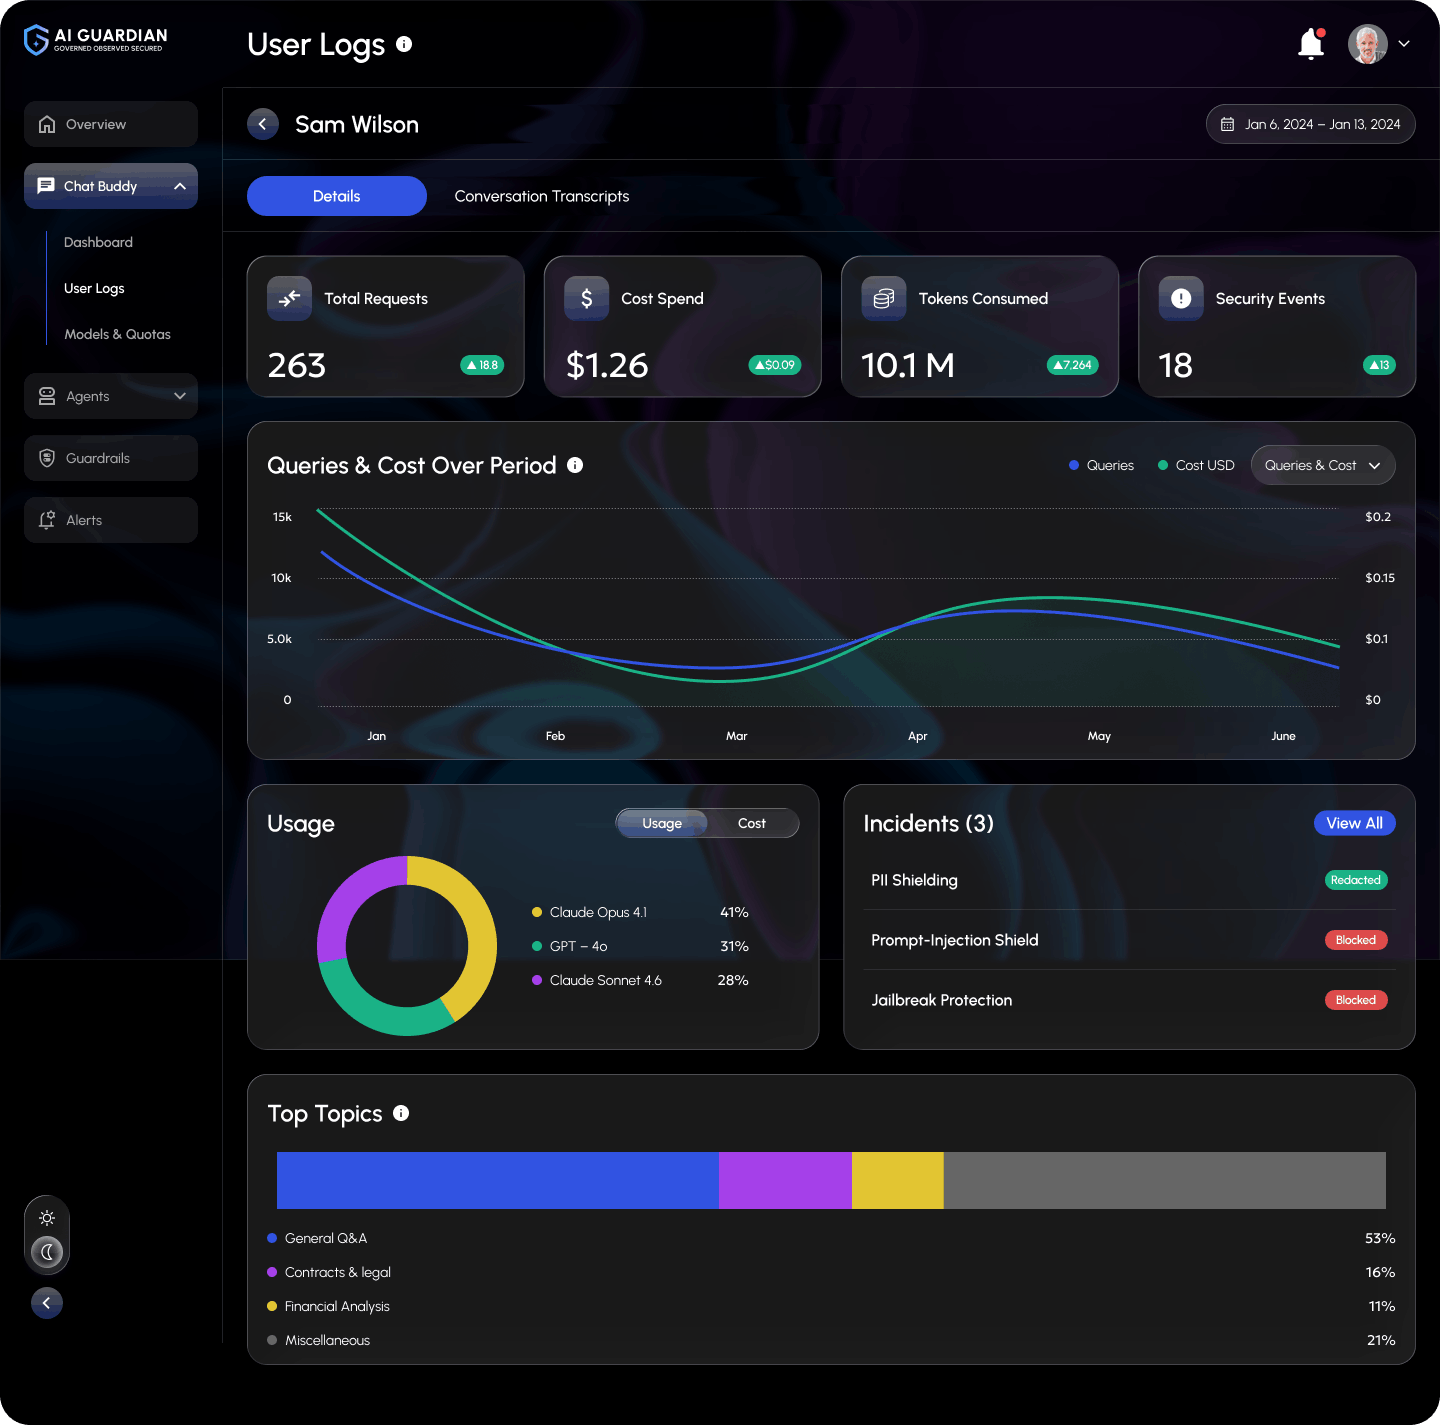
Run these four checks before you sign.
- Test your own files: Upload your own multi-page files and ask the vendor to report what it missed.
- Find the blocked request: Show a blocked request in the audit log, with the user named.
- Break inspection on purpose: Ask whether traffic fails open or closed when inspection stops working.
- Measure the overhead: Measure added latency on your own prompts, and count false positives.
How do AI guardrails platforms compare? Five approaches for 2026
Most guardrail products fall into one of five approaches. Pick the approach first, then shortlist products inside it. Each entry names the job it does best and where it stops, including ours.
1. Control plane (Folio3 AI Guardian)
- Best for: Governing employee and agent AI across every team from one policy.
- How it works: Five checks run before every answer: identity, inspection, routing, orchestration, and audit.
- Strengths: Multi-page file masking, role-based model routing with department caps, and department and executive dashboards.
- Where it stops: A single engineering team that only needs an in-app prompt-injection API.
2. Open-source frameworks
- Best for: Programmable rails inside one application.
- How it works: Python packages let engineers write input, dialog, and output rules in code.
- Strengths: Full control and no license fee.
- Where it stops: Teams without engineers to run, update, and tune them, and any need for company-wide policy.
3. Cloud-native guardrails
- Best for: Models hosted in one cloud.
- How it works: Each major cloud offers content filters, denied topics, and sensitive-data filters for its own models.
- Strengths: Quick to switch on inside that cloud.
- Where it stops: Models spread across several providers, and staff who use tools outside that cloud.
4. Point security tools
- Best for: One narrow risk, such as prompt injection or data leakage.
- How it works: Specialist products defend a single threat.
- Strengths: Depth on that one threat.
- Where it stops: An employee workspace, spend controls, or routing.
5. AI gateways, open-source and commercial
- Best for: Developer traffic to models.
- How it works: A gateway routes calls and applies limits, and many add guardrails, identity, budgets, or agent controls, either built in or through outside guardrail providers.
- Strengths: One endpoint for backend model calls, with PII, injection, and policy checks in many current products.
- Where it stops: Knowing which employee made each request, or giving staff a ready workspace and executive reporting, which varies by product.
Approach comparison
| Capability | Control plane (AI Guardian) | Open-source framework | Cloud-native | Point security tool | Gateway |
|---|---|---|---|---|---|
| Employee workspace | Teams, Slack, web, mobile | No | No | No | Varies by product |
| PII handling | Prompts and multi-page files | Via validators or integrations | Text filters, within that cloud | Data leakage defense | Varies, from basic to built-in masking |
| Prompt injection defense | Inspection step | Via validators | Provider filters | Core strength | Built in or via integrated providers |
| Off-domain blocking | Role-based policy | Topical rails you write | Denied topics | Not a focus | Varies by product |
| Role-based routing and spend caps | Yes | No | Limited to that cloud | No | Routing yes; confirm budgets and quotas |
| Agent governance | Governed chains, identity inherited | You build it | Limited | Varies | Varies |
| Private cloud deployment | Your Azure or AWS tenant | Self-hosted | That cloud only | Varies | Self-hosted or SaaS |
| Who runs it | Vendor builds, runs in your tenant | Your engineers | Provider | Vendor | Your engineers or vendor |
Source note: Ratings are Folio3's general assessment of each approach, and individual products vary. Check current vendor documentation before you decide.
See AI Guardian govern a live request
Comparison tables only go so far. Watch one employee prompt pass through identity checks, PII masking, model routing, and audit logging before the answer comes back, using your own sample data.
When AI Guardian is the right fit
It fits best when staff and agents use AI every day, and security, IT, and finance need one set of rules. It is not the right pick for every team, and the comparison above shows where it is not. Six traits matter for that fit.
- More than a prompt filter: It adds identity, routing, budgets, and audit to inspection.
- More than an API gateway: It governs people and agents, not only backend calls.
- One governed workplace: Staff use approved models in Teams, Slack, web, and mobile, so the governed path is also the convenient one.
- Guardrails plus spend governance: Department caps and role-based routing sit in the same policy as data rules.
- Governs agents you already run: Multi-agent chains run under the requester's identity, with the same masking and audit as a prompt.
- Built for department-level control: Line-of-business heads set their own quotas and model access without engineering tickets.
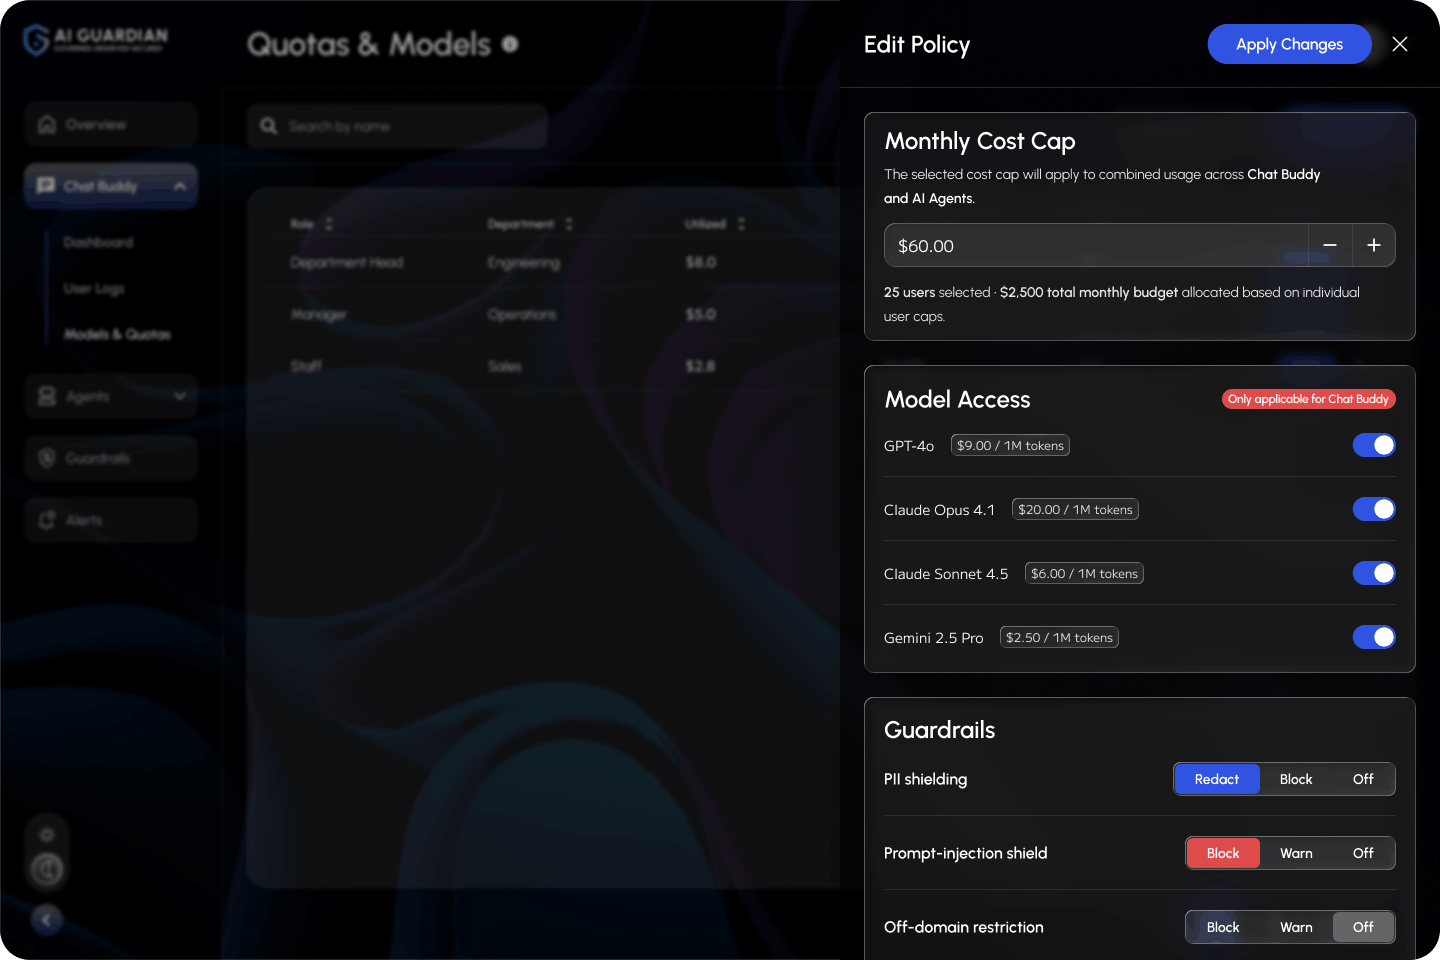
Five controls before every answer
IMAGE_URL_HERE in this block's data-image-url attribute with your final image link.
IMAGE_URL_HERE
- Identity: SSO matches the user to a role, department, and policy set.
- Inspection: Prompts and documents are scanned for PII, secrets, and injection attempts, then masked or blocked.
- Routing: Policy checks department quotas, user permissions, and model access, then sends the request to the approved model.
- Orchestration: Specialized agents collaborate, retrieve company knowledge, and run approved actions under the same rules.
- Audit: Token use, cost, policy decisions, and model activity are logged against a named user.
Worked example: Here is one request, with fictional identifiers. A finance analyst uploads a vendor invoice and asks to check the IBAN and Iqama number against the vendor record, then adds a request to plan a weekend trip. Inspection replaces both identifiers with placeholders before the request leaves the tenant. Policy blocks the trip request as off-domain and logs it, and the invoice task continues on the approved mid-tier model.
What AI Guardian does not guarantee
No guardrail catches every injection attempt, and no platform can guarantee that employees never use unmanaged tools. Keep adversarial testing, output review, and human oversight in your program, and treat model output as untrusted input.
How do AI guardrails cut AI spend, not just risk?
IMAGE_URL_HERE in this block's data-image-url attribute with your final image link.
IMAGE_URL_HERE
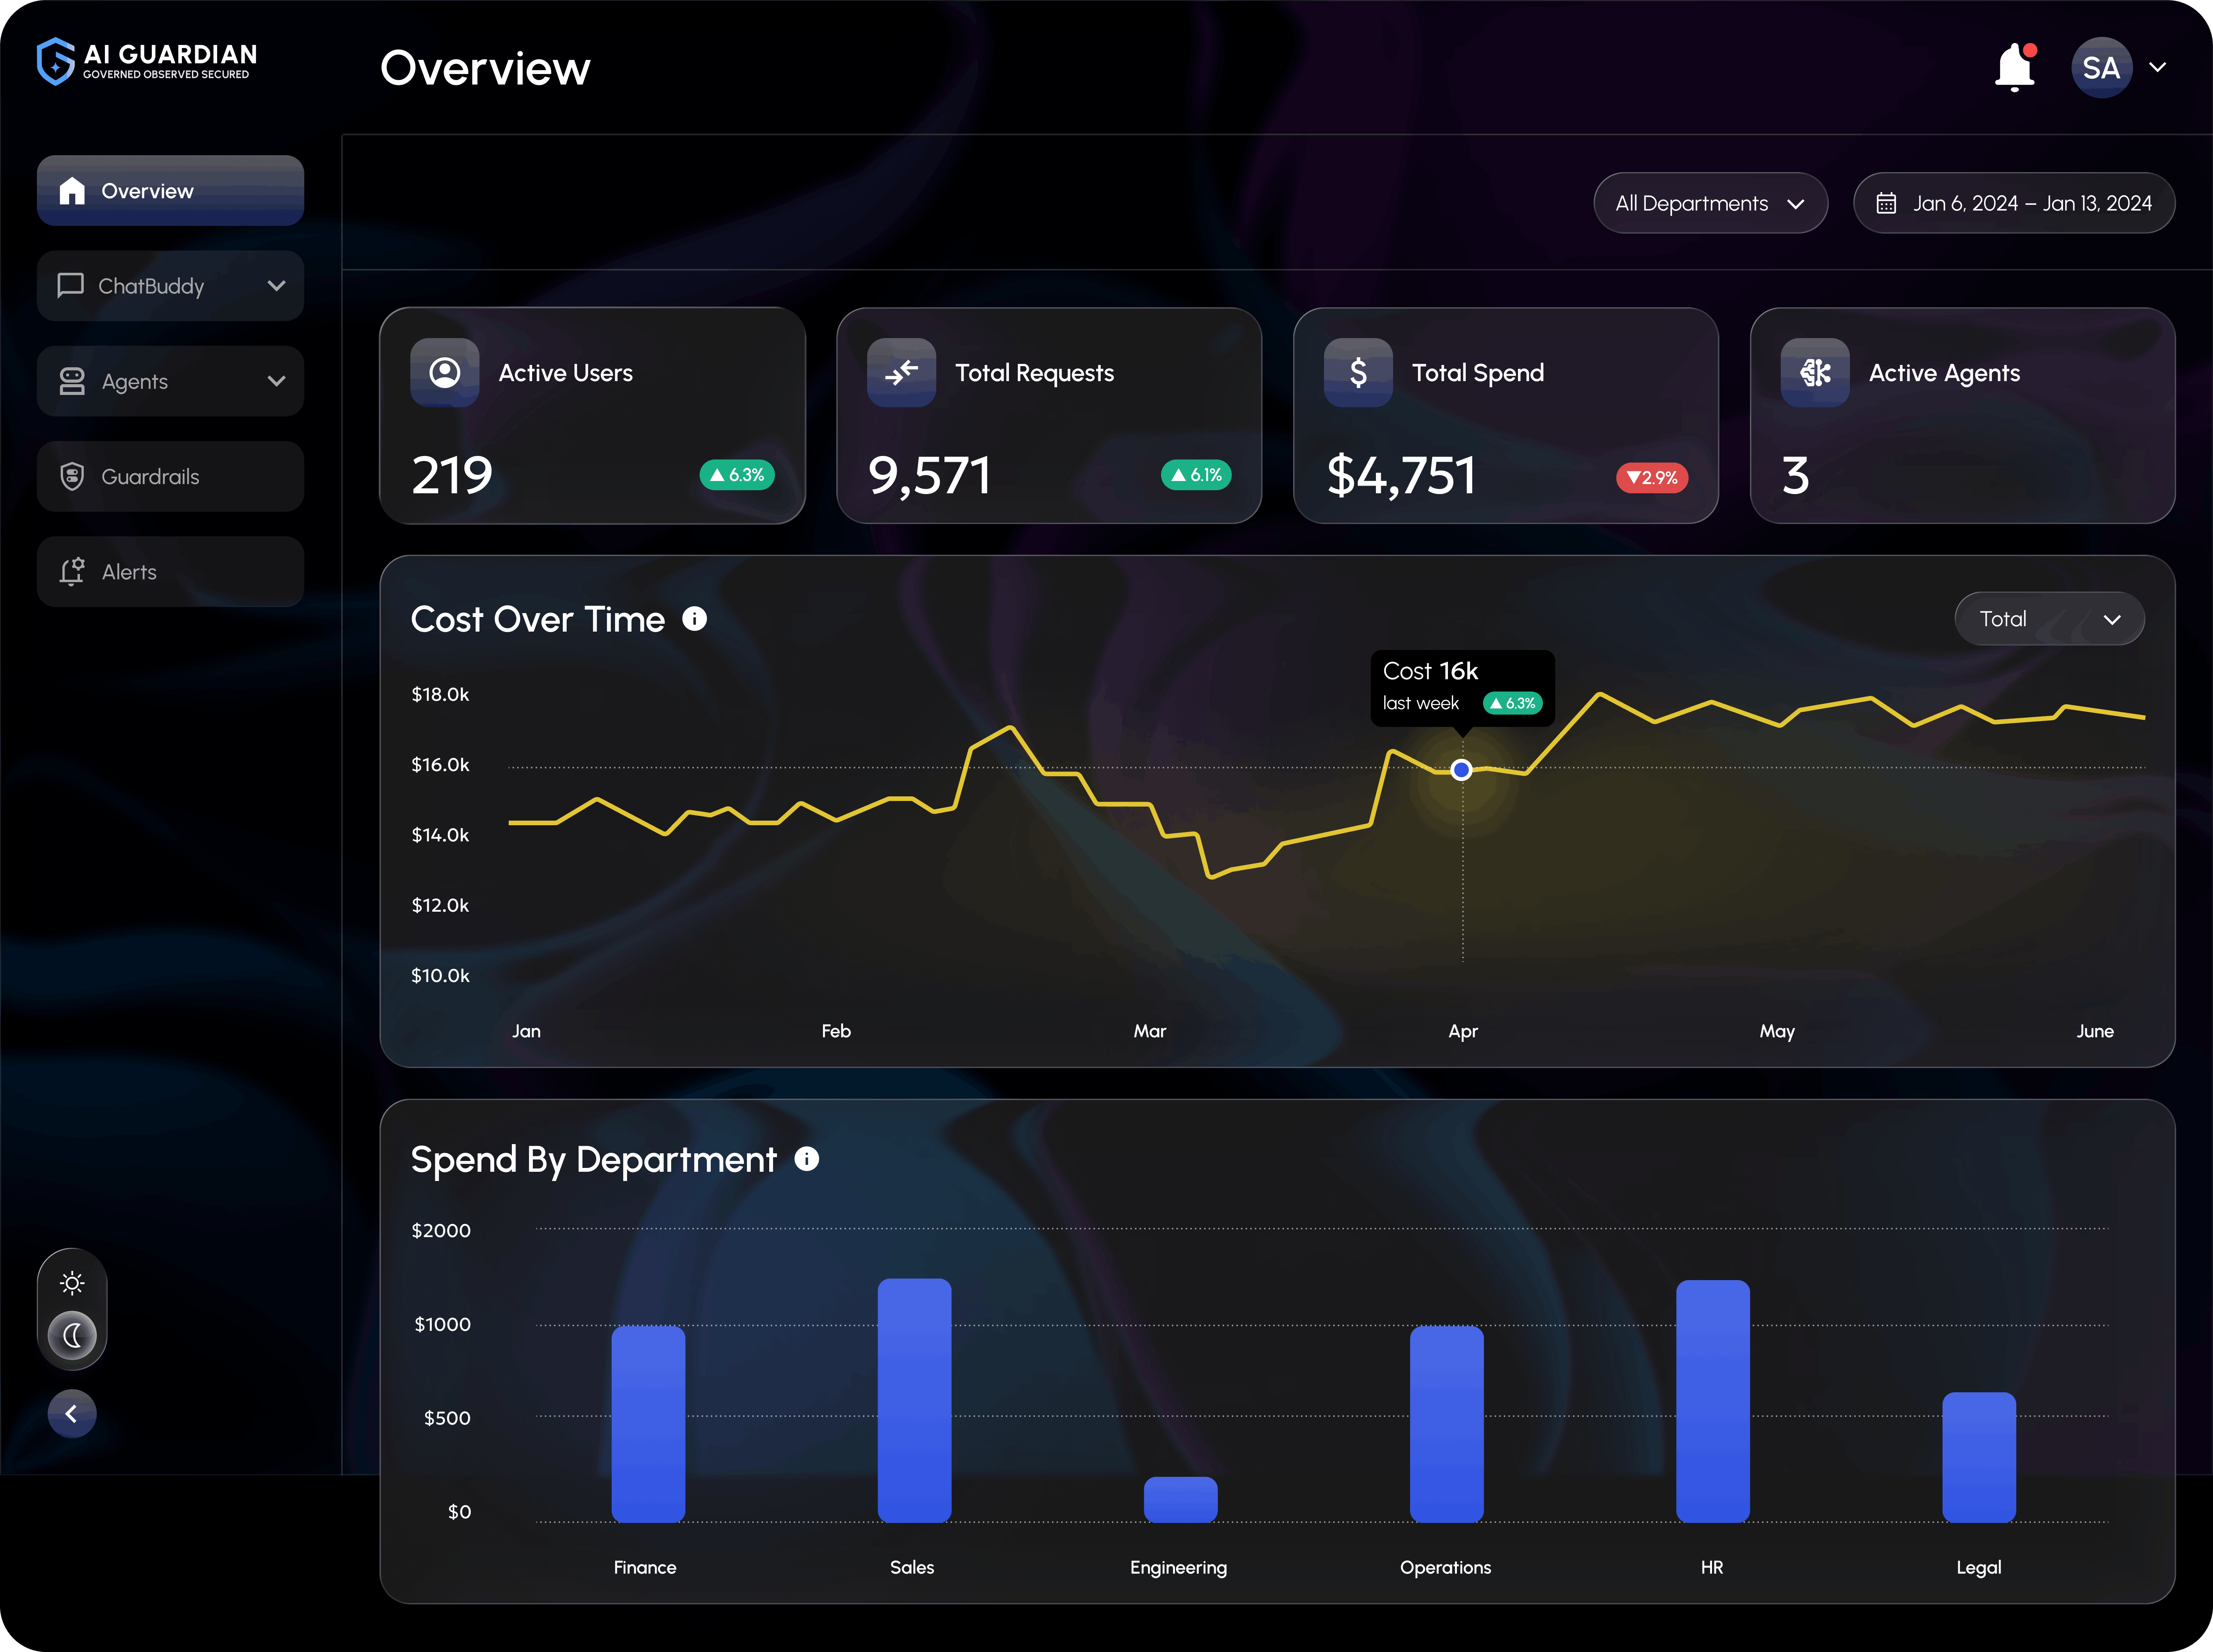
Most AI spend comes from routine work sent to expensive models. Guardrails that act on cost turn a risk control into a budget control.
- Role-based model tiers: General staff draft and look things up on efficient models, analysts review documents on mid-tier models, and legal and engineering use frontier models for complex reasoning under quotas.
- Department monthly caps: Dollar and token limits give every budget a named owner.
- Off-domain blocking: Declining non-business requests keeps organization-funded capacity off personal tasks.
- Request-level cost traces: Every record ties tokens and cost to a user, so finance sees who spent what.
Microsoft's own model router documentation describes the same principle: smaller, cheaper models handle simple prompts, and frontier models are reserved for complex tasks.
Modeled scenario: AI Guardian's model shows about 30% lower blended spend in a modeled mixed-workload scenario that rests on stated assumptions. It is a scenario, not a benchmark and not a guarantee. Track cost per completed task rather than cost per token, since a cheaper model can cost more per finished task.
How to roll out AI guardrails: steps, pricing, and metrics
Start with one department, then extend the same controls across the company.
- Inventory use: List the AI tools, models, and agents in use, approved or not.
- Pick one department: Choose a team with real data and a willing owner.
- Set guardrails and quotas: Agree on what is allowed, restricted, and prohibited.
- Test: Run sample requests through every control and check the audit log.
- Extend: Reuse the same policy set for the next team.
Phase 1: Align (2 to 4 hour sessions)
Requirements and alignment sessions record policies, hierarchy, roles, model access, and quotas.
Phase 2: Configure and deploy (4 to 5 business days)
AI Guardian goes live in 4 to 5 business days after alignment, with timing varying by organizational complexity and integrations.
Pricing
AI Guardian currently starts at $15K for one-time implementation and $8K per quarter for the platform license. Final pricing depends on scope, lines of business, integrations, and deployment requirements. Compare vendors on implementation and recurring license as separate figures, and add hosting and engineering time for open-source options.
Metrics leadership can use
| Metric | What it shows |
|---|---|
| Share of AI traffic on the governed path | Whether shadow AI is shrinking |
| Blocked, redacted, and warned requests by policy | Where policy applies pressure |
| Spend per department against cap | Budget ownership |
| Cost per completed task | Quality of model assignment |
| Time to revoke a user's or agent's access | Containment readiness |
Start with one department, scale to every team
Pick one team, set its guardrails and quotas, and see the audit trail within days. The same controls extend to every other department.
AI guardrail use cases by function
| Function | Risk | Guardrail applied |
|---|---|---|
| Finance and banking | IBANs and account data pasted into prompts | Masking before the model call |
| Legal and compliance | Contract text sent to public models | Review inside an approved workspace with redaction |
| IT and security | Scattered personal AI accounts | One governed workspace behind SSO |
| Software and SaaS teams | Source code and secrets in prompts | Secret scanning and role-based model access |
Which compliance frameworks do AI guardrails support?
Guardrails supply evidence for these frameworks. They do not make an organization compliant with any of them.
| Framework | What it asks for | AI Guardian control | Evidence produced |
|---|---|---|---|
| EU AI Act, Article 12 | High-risk systems must technically allow automatic recording of events (logs) | Audit | Per-request logs tied to a user |
| ISO/IEC 42001 | An AI management system with policies, roles, and audit | Identity, policy | Role mapping and policy decisions |
| NIST AI RMF | Govern, Map, Measure, Manage | Policy, audit | Policy records and usage reports |
| OWASP Top 10 for LLMs | Defenses for injection and sensitive data disclosure | Inspection | Block and mask events |
| GDPR, Article 5(1)(c) | Personal data limited to what is necessary | Inspection | Masking record per request |
Folio3 is ISO 27001 certified. That certification covers organizational information security management, so prompt-level assurance comes from the controls above.
Frequently asked questions
What is an AI guardrails platform?
It is software that enforces policy on AI inputs and outputs at runtime. It inspects each request and response, blocks or masks what breaks the rules, and records the decision.
What is the difference between AI guardrails and an AI gateway?
A gateway routes model traffic, and many current gateways also add guardrails, identity, and budgets. Guardrails are the policy layer that checks what the traffic contains, such as PII, injections, topics, and spend, whether they run inside a gateway or beside it.
How do AI guardrails differ from AI governance?
Governance sets policy, ownership, and oversight, and governance platforms may focus primarily on policy, inventory, and oversight rather than inline enforcement. Guardrails enforce those rules on live requests and record the evidence.
Can AI guardrails prevent prompt injection attacks?
They reduce exposure but cannot catch every attempt. Keep output validation and adversarial testing in the program, and treat model output as untrusted input.
Do AI guardrails platforms redact PII in uploaded documents?
Some do, and many cover only pasted text. Test multi-page files and regional identifiers on your own samples, and ask what the platform missed.
Are agent guardrails different from LLM guardrails?
Yes. LLM guardrails check prompts and responses, while agent guardrails also control tools and actions through allowlists, identity inheritance, and approval gates.
Should I use open-source or commercial AI guardrails?
Open source suits teams with engineers who can run and tune it. Commercial platforms suit teams that want governance, support, and reporting without building them.
Do AI guardrails slow users down?
Inspection adds some processing time, and the amount depends on the product and your traffic. Measure latency and false positives on your own prompts before you commit.
Put guardrails where your teams already use AI
Employees will use AI with or without approval, so give them a governed path. AI Guardian builds in redaction, approved models, spend limits, and audit evidence, and your risk, IT, and finance leaders see every request in one place. Book a demo to see it run on your own sample prompt.
See AI Guardian run on your own sample prompt
Listed on Microsoft Marketplace. ISO 27001 certified. 20+ years and 950+ projects delivered. Same-day response.
Written by the Folio3 AI Editorial Team. Technical content on guardrail types, frameworks, and controls was reviewed by Abdul Sami, Head of AI Development at Folio3 AI, in October 2026.

