


On this page
AI risk management software finds, controls, and documents the risks that AI systems create inside an organization: data leaks into prompts, unapproved tools, biased or unexplainable outputs, and gaps against regulation. Security, compliance, and risk teams buy it. It is a different product from software that uses AI to score fraud or credit risk.
The need is measurable. IBM's 2026 Cost of a Data Breach Report found that 68% of breached organizations lacked AI governance policies to manage AI or detect shadow AI, up from 63% a year earlier. The share of security incidents involving shadow AI more than doubled, from 20% to 43%. This guide covers the risk categories, the frameworks to map to, how the software works, and what to check before buying.
What is AI risk management software?
AI risk management software is a platform that inventories AI systems, scores their risk, enforces controls, monitors behavior, and produces audit evidence. The term covers two different products, and knowing which one you need saves weeks of evaluation.
Managing the risk of AI
This is the governance side of the problem. The software monitors your AI systems and the people using them, catching data leaks, unapproved tools, policy violations, and compliance gaps before they become audit findings. Security, compliance, and risk teams are the typical buyers.
Choose this if the question is: “Can we prove our AI use is safe and compliant?”
Using AI for risk management
This is AI-assisted risk management software, where machine learning models score fraud, credit risk, and operational risk faster and more consistently than rule-based systems can. Banks and insurers use it to flag suspicious transactions in real time or rate loan applicants at scale.
Choose this if the question is: “Can we detect fraud, credit or operational risk faster?”
The rest of this guide covers the first category, because that is where AI-specific regulation such as the EU AI Act applies.
Buy vs build: how organizations approach AI governance
Most organizations choose between buying a governance platform and building their own controls. Buying gets controls running sooner, while building gives full control at the cost of an engineering team that owns the system for as long as it runs.
| Factor | Buy a governance platform | Build custom software |
|---|---|---|
| What happens before controls go live | Configuration, identity provider connection, and policy setup. No code is written. | Architecture design, engineering, security review, and testing before the first control runs. |
| Blocking and redaction at request time | Available in gateway and runtime products. Program-layer platforms document risk and hand blocking to a separate tool. | Available only if the team builds a proxy into the path between users and models. |
| Keeping framework mappings current | The vendor updates mappings when rules change, such as the 2026 Omnibus moving EU AI Act high-risk dates. | An internal owner has to track each regulatory change and re-map controls by hand. |
| Audit evidence | Identity-attributed logs and framework reports come built in. | The team designs the log schema, retention rules, and every report an auditor will request. |
| New models and providers | Vendor adds connectors as model providers release or retire models. | Each new model or provider API is an engineering ticket. |
| Where prompts and logs are stored | Depends on the deployment model. Ask whether it runs as vendor SaaS or inside your own cloud tenant. | Wherever the team deploys it, with full control over residency. |
| Cost pattern | License plus implementation, with predictable renewal costs. | Engineering time up front, then ongoing maintenance, hosting, and on-call support. |
| Choose it when | Your obligations map to NIST AI RMF, ISO/IEC 42001 or the EU AI Act, and you need controls running this quarter. | You face regulatory, data-residency, or model requirements no product covers, and have engineers to own the system long term. |
Many teams land in between: they buy a platform for identity, redaction, and audit evidence, then build only the integrations or policies specific to their own environment.
Start with the control layer you actually need
Use the buying criteria later in this guide to test enforcement, deployment, integrations, framework coverage, and audit output before comparing feature lists.
Why AI risk management can't wait
Three pressures now overlap: employees use AI without approval, EU AI Act deadlines have fixed dates, and penalties reach board level. IBM's 2026 data shows governance losing ground while AI exposure grows.
Most organizations did not adopt AI through a formal policy decision. It arrived through individual tools: a chatbot approved for one team, a coding assistant picked up by developers, a contract summarizer that spread across departments before IT knew it existed. By the time governance becomes a priority, AI is already embedded in daily workflows.
Shadow AI is already inside the business.
IBM's 2026 report found that security incidents involving shadow AI rose from 20% to 43%, while the share of organizations requiring IT approval before deploying AI fell from 45% to 38%—restrictions without a usable approved alternative push people toward less visible workarounds.
Regulators have set firm dates.
The Digital Omnibus on AI (Regulation (EU) 2026/1744) was published in the Official Journal on 24 July 2026 and entered into force on 27 July 2026, resetting several EU AI Act deadlines.
EU AI Act transparency duties under Article 50 apply from 2 August 2026, with a transition to 2 December 2026 for machine-readable marking on generative systems already on the market. High-risk obligations for stand-alone (Annex III) systems now start on 2 December 2027, and on 2 August 2028 for AI embedded in regulated products. Prohibited practices have applied since 2 February 2025.
Penalties are board-level numbers.
A prohibited AI practice under the EU AI Act can carry a fine of up to EUR 35 million or 7% of global annual turnover, whichever is higher (Article 99).
Access controls are widely missing.
In IBM's 2026 report, 92% of organizations that had an AI-related breach lacked proper AI access controls such as role-based access and multifactor authentication. Only 19% of breached organizations reported that their governance and security teams coordinate on AI. The 2025 report put the access-control figure at 97%.
The AI risk categories this software manages
AI risk is a set of distinct failure modes that appear at different points in a model's lifecycle, from training data to production decisions. Each needs its own control, and the table maps one to the other.
| Risk | What it looks like | Governance response |
|---|---|---|
| Model bias | Skewed outcomes for certain user groups caused by gaps or imbalances in training data. | Pre-deployment fairness testing and periodic re-testing against live data as it evolves. |
| Explainability gaps | A model produces a decision that affects a customer, but no one on the team can reconstruct why the model reached it. | Model documentation, decision logs, and mandatory human review for high-stakes outcomes. |
| Model drift | Accuracy degrades over time after deployment as real-world data patterns shift away from training conditions. | Performance monitoring with defined drift thresholds and retraining triggers assigned to a named team. |
| Data privacy exposure | Employees paste customer records, financial details, or sensitive identifiers into prompts that reach an external model's infrastructure. | PII detection and redaction at the point of request, before data leaves the environment. |
| Shadow AI | Employees use personal accounts, unapproved tools, or free-tier services without organizational oversight. | One approved access point with SSO enforcement, a maintained tool inventory, and a clear usage policy. |
| Adversarial and agent risk | A prompt injection changes a model's behavior, or an AI agent holds broader permissions than its task needs. | Input inspection, least-privilege access for agents, action limits, and security event logging. |
| Regulatory non-compliance | A system falls into a regulated risk category without the documentation, oversight, or controls that category requires. | Risk classification at intake, framework mapping during assessment, and audit-ready records maintained throughout. |
| Uncontrolled AI spend | Frontier models handle routine, low-complexity work with no team tracking what it costs or why. | Role-based model routing, per-department spend caps, and cost attribution per request. |
See how AI Guardian applies controls to each request
Identity, inspection, policy enforcement, routing, spend controls, agent governance, and audit traces sit in one governed request path.
AI risk management frameworks explained.
Three frameworks come up most in buying conversations: NIST AI RMF for structure, ISO/IEC 42001 for certification, and the EU AI Act for legal obligations. The software's job is to produce evidence against them.
NIST AI RMF
Published in January 2023, the NIST AI Risk Management Framework is a voluntary resource widely adopted by US organizations. It organizes governance work into four functions that build on each other:
- Govern: Sets the policies, roles, and lines of accountability that underpin every other activity in the framework.
- Map: Establishes context for each AI system in use, including its purpose, intended users, data sources, and who would be affected if it failed.
- Measure: Identifies, analyzes, and tracks risks using a combination of quantitative metrics and qualitative assessment methods.
- Manage: Prioritizes identified risks, applies appropriate treatments, and determines what to continue monitoring, what to accept, and what to retire.
NIST also publishes a Generative AI Profile (NIST AI 600-1, July 2024) that names twelve risks unique to or worsened by generative AI, and it is additive to the base framework. NIST has said AI RMF 1.0 is being revised, so check the NIST AI RMF page for the current version before citing controls.
ISO 42001
ISO/IEC 42001:2023 is the first certifiable international standard for AI management systems, built around a Plan-Do-Check-Act cycle that an accredited auditor can certify against, similar in structure to ISO 27001.
- Clauses 4 to 10: Cover the management system itself, including organizational context, leadership commitment, planning, support resources, operational execution, performance evaluation, and continual improvement.
- Annex A: Provides reference controls across AI policy, data management, system lifecycle, stakeholder communication, and third-party relationships.
- Audit evidence: Achieving and maintaining certification depends on documented risk assessments, impact assessments, and demonstrable evidence that monitoring activities run on a defined and repeatable schedule.
Certification applies to an organization's AI management system, not to a software product, so a vendor can support your certification but cannot give it to you.
EU AI Act
The EU AI Act is enforceable law, not guidance. It applies to any organization that places AI systems on the EU market or whose AI outputs are used in the EU, wherever it is headquartered. Obligations rise with the risk tier.
| Risk tier | Examples | What applies | Timing |
|---|---|---|---|
| Prohibited | Social scoring, manipulative techniques, untargeted facial image scraping | Banned outright | Since 2 February 2025. A further prohibition on AI that generates non-consensual intimate imagery or child sexual abuse material applies from 2 December 2026. |
| High-risk | AI used in hiring, credit scoring, education and critical infrastructure | Risk management system, data governance, logging, human oversight, conformity assessment | 2 December 2027 (Annex III); 2 August 2028 (Annex I products) |
| Limited risk | Chatbots and AI-generated content | Transparency obligations: disclose AI interaction and label synthetic content | From 2 August 2026. Machine-readable marking of generative output on systems already on the market: 2 December 2026. |
| Minimal risk | Spam filters, AI in video games | No specific obligations under the Act | Not applicable |
One control set, multiple frameworks
Mapping each control once and tagging the framework obligations it satisfies avoids repeating the same evidence work for NIST, ISO 42001, and the EU AI Act. One AI system inventory serves all three. Folio3's data and AI security services map client controls to NIST AI RMF, the EU AI Act, SOC 2, and ISO 27001 Annex A in the same way.
| Control | NIST AI RMF | ISO 42001 | EU AI Act |
|---|---|---|---|
| AI system inventory | Map | Annex A resource and lifecycle controls | Technical documentation and registration |
| Risk and impact assessment | Map, Measure | Clause 6, Annex A impact assessment | Risk management system (Article 9) |
| Logging and audit trail | Measure, Manage | Clause 9 performance evaluation | Record-keeping (Article 12) |
| Human oversight | Govern, Manage | Annex A use of AI systems | Human oversight (Article 14) |
How AI risk management software works
Most solutions follow the same five-step cycle. What separates products is how much of each step is automated, and how much visibility it surfaces without manual effort.
Identify
Before risk can be managed, every AI system in use needs to be on record: models, agents, API integrations, and third-party tools. Solutions that route all AI traffic through a central access point build this inventory automatically, catching tools that teams adopt informally and never declare to IT or security.
Assess
Each system is scored based on what data it processes, which user populations it affects, and which regulatory obligations apply. That score drives two decisions: what controls the system needs before it can operate, and how frequently it needs to be reviewed as usage patterns change.
Mitigate
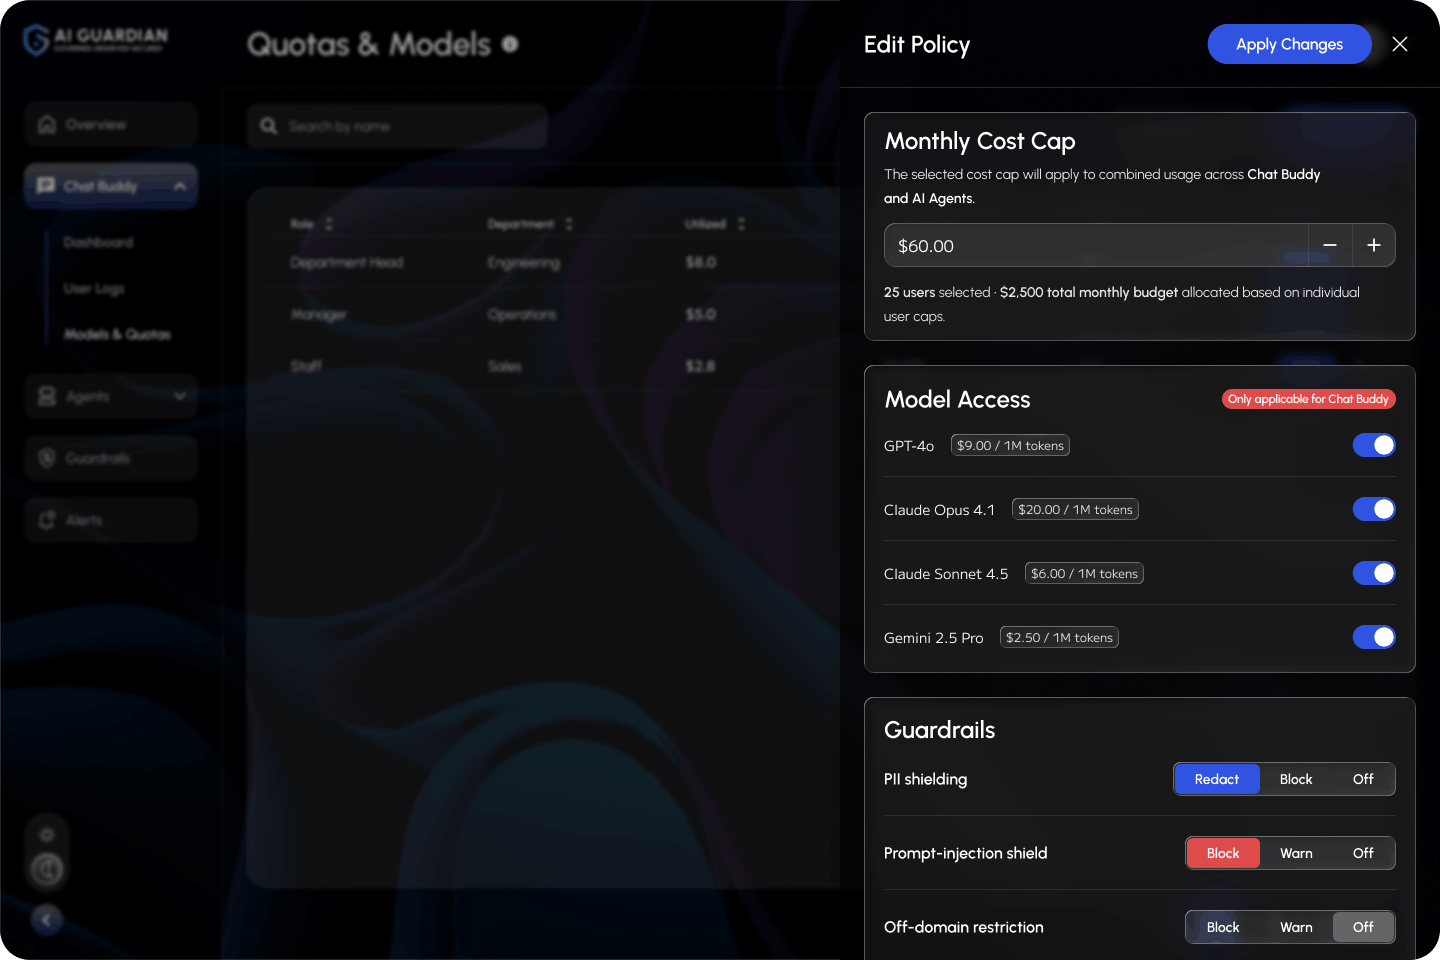
Controls are applied in proportion to assessed risk, not uniformly across the board. A low-risk internal summarization tool gets different treatment than a customer-facing agent handling PII. Typical controls include content filtering, prompt injection protection, PII redaction, role-based model access, and agent action limits.
IMAGE_URL_HERE in this block's data-image-url attribute with your final image link.
IMAGE_URL_HERE
Monitor
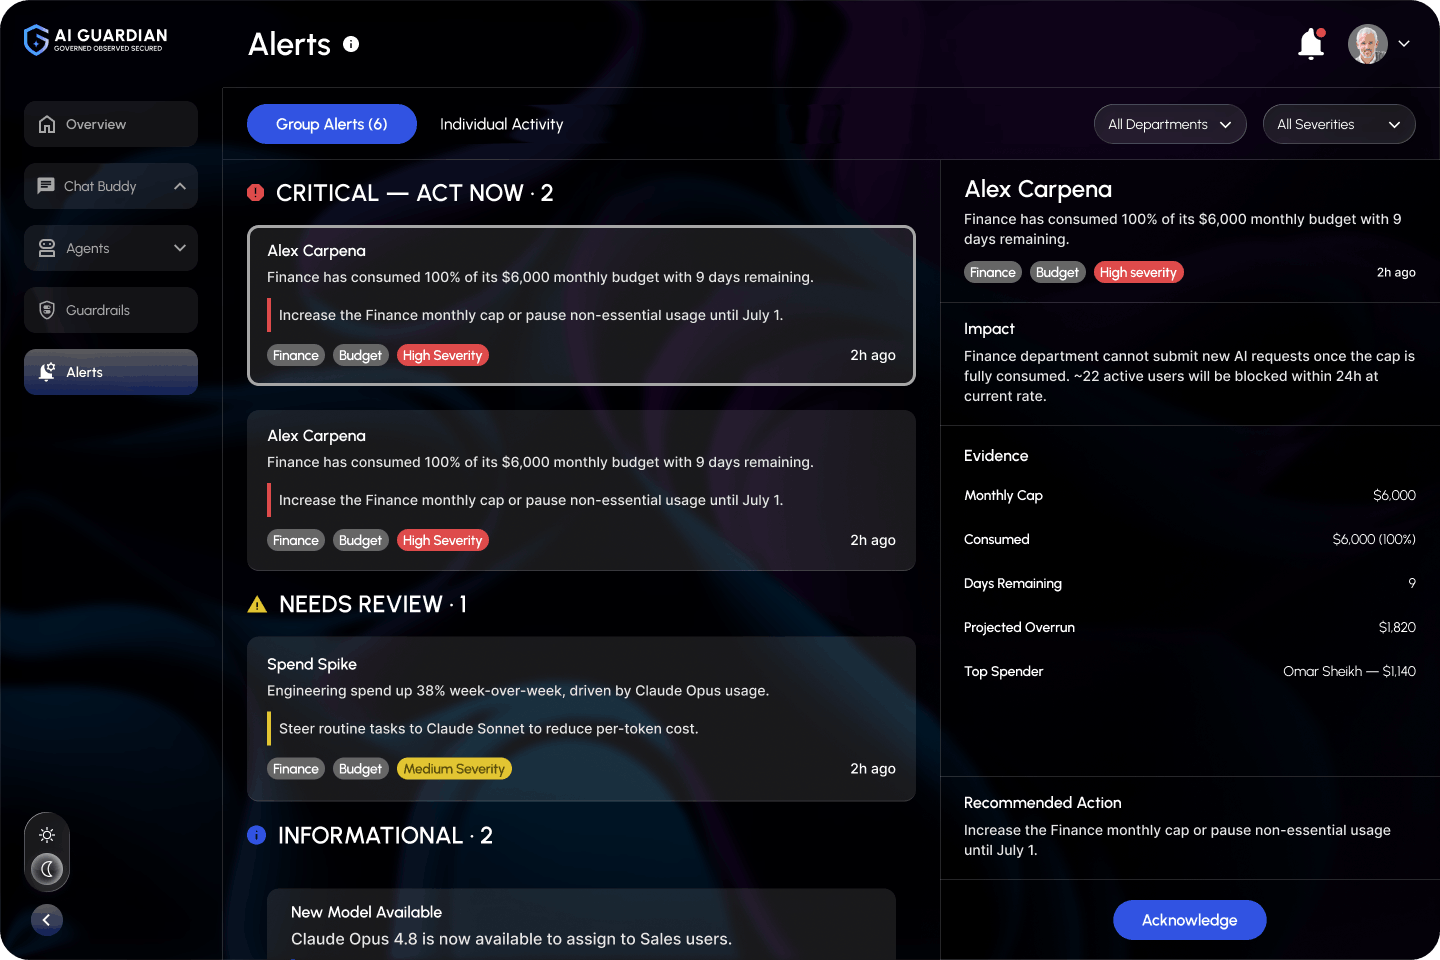
Controls keep running after deployment. Policy violations, blocked requests, unusual spend, and odd output patterns are tracked as they happen, and severity ranking keeps responders on the events that matter.
Report
Raw operational logs become records that auditors and leadership can use: who accessed which model, what was blocked and why, how each control maps to a specific framework requirement, and whether the organization's risk posture has changed over the reporting period.
Illustrative example: one request through the cycle
An employee pastes a customer contract into a chat assistant.
- Identify: The request appears in the AI inventory under that user and tool.
- Assess: Contract data raises the system's risk score.
- Mitigate: Names and account numbers are masked before the request reaches the model.
- Monitor: The request is logged with user, model, tokens, and cost.
- Report: The log becomes evidence for record-keeping and oversight duties.
See how AI Guardian handles a request from start to finish.
See What AI Guardian Monitors
Follow the same request path from identity and inspection through policy enforcement, routing, spend, and audit trace.
Common challenges in AI risk management implementation
Most governance programs stall on ownership and adoption, not on tooling.
Fragmented model inventory
AI usage is spread across SaaS platforms, internal notebooks, and personal accounts IT never approved. Without a consolidated view, every risk assessment starts with incomplete information.
Integration gaps
A governance tool that sits outside the existing identity provider and GRC platform quickly becomes another console teams stop checking. A control nobody opens does not reduce risk.
Alert fatigue
Monitoring systems that flag everything with equal urgency train teams to stop paying attention. Severity ranking and clear ownership matter as much as detection capability.
IMAGE_URL_HERE in this block's data-image-url attribute with your final image link.
IMAGE_URL_HERE
Manual documentation
Audit evidence assembled by hand under deadline pressure is slow and hard to repeat. Evidence pulled automatically from operational logs is faster and more defensible.
Employee workarounds
Controls that make approved AI slower than a personal account push people back toward shadow AI. If approved AI is slower than a personal account, people will use the personal account.
Split ownership
IBM's 2026 report found that only 19% of organizations coordinate governance and security teams on AI. Name one accountable owner for AI risk and hold a shared review, so policy and enforcement do not drift apart.
Which type of AI governance tool do you need?
AI governance tools sit in different layers, and each is strong in one. Picking the layer that matches your biggest gap matters more than picking the longest feature list.
| Layer | What it does | Usually strong at | Common gap |
|---|---|---|---|
| Program and GRC platforms | Policy, AI inventory, assessments, audit evidence | Framework mapping, approvals, regulator-facing documentation | Blocking at request time is often delegated to another product. |
| Observability and model monitoring | Tracks drift, quality, bias, and performance on models | Model-level evidence | Does not govern how employees use external AI tools. |
| AI security | Detects attacks and misuse against AI systems | Adversarial testing, prompt injection defense | Not built for policy documentation. |
| Gateway and runtime control | Sits in the request path: identity, redaction, routing, spend, audit trace | Enforcing policy on every request, the AI Guardian way | Does not replace model-level bias testing or drift monitoring. |
What to look for in AI risk management software
Evaluating AI governance tools comes down to six capabilities. Ask each vendor to demonstrate them instead of describing them, and you can use these six questions as your vendor checklist.
- Guardrail and PII controls: Send a test prompt containing a fake IBAN and confirm it is masked before it reaches the model. Reporting after the fact leaves data already exposed.
- Enforcement layer: Ask whether the product blocks at request time or only documents. If it documents only, ask what it pairs with to enforce.
- Framework coverage: Ask which frameworks are mapped today: NIST AI RMF, ISO/IEC 42001, and the EU AI Act. One mapped control set saves the most effort at audit time.
- Deployment model: Confirm prompts and logs stay in your own cloud tenant. Any path through vendor infrastructure raises a data residency question.
- Integration reach: Confirm native connection to your identity provider, collaboration tools, and GRC stack. A standalone console that needs manual cross-referencing gets ignored under pressure.
- Audit output: Ask for a sample log. It should be identity-attributed and structured enough for an auditor to use without reformatting.
Test the six checks on your own AI use cases
Use sample prompts, your cloud requirements, your identity stack, and your framework scope to see whether the controls work before you buy.
What drives the cost of AI risk management software?
Price depends on scope more than on the product name. These are the factors that move a quote, and the questions to ask any vendor.
- Number of AI systems, models, and agents governed
- Number of users, and whether pricing is per seat, per model, or per platform
- Deployment model: vendor-hosted SaaS or inside your own cloud tenant
- Integrations required: identity provider, GRC, ticketing, collaboration tools
- Frameworks in scope and how much configuration each needs
- Implementation services, and whether they are included or billed separately
- Ongoing tuning as models and regulations change
Inside AI Guardian: what it monitors and controls
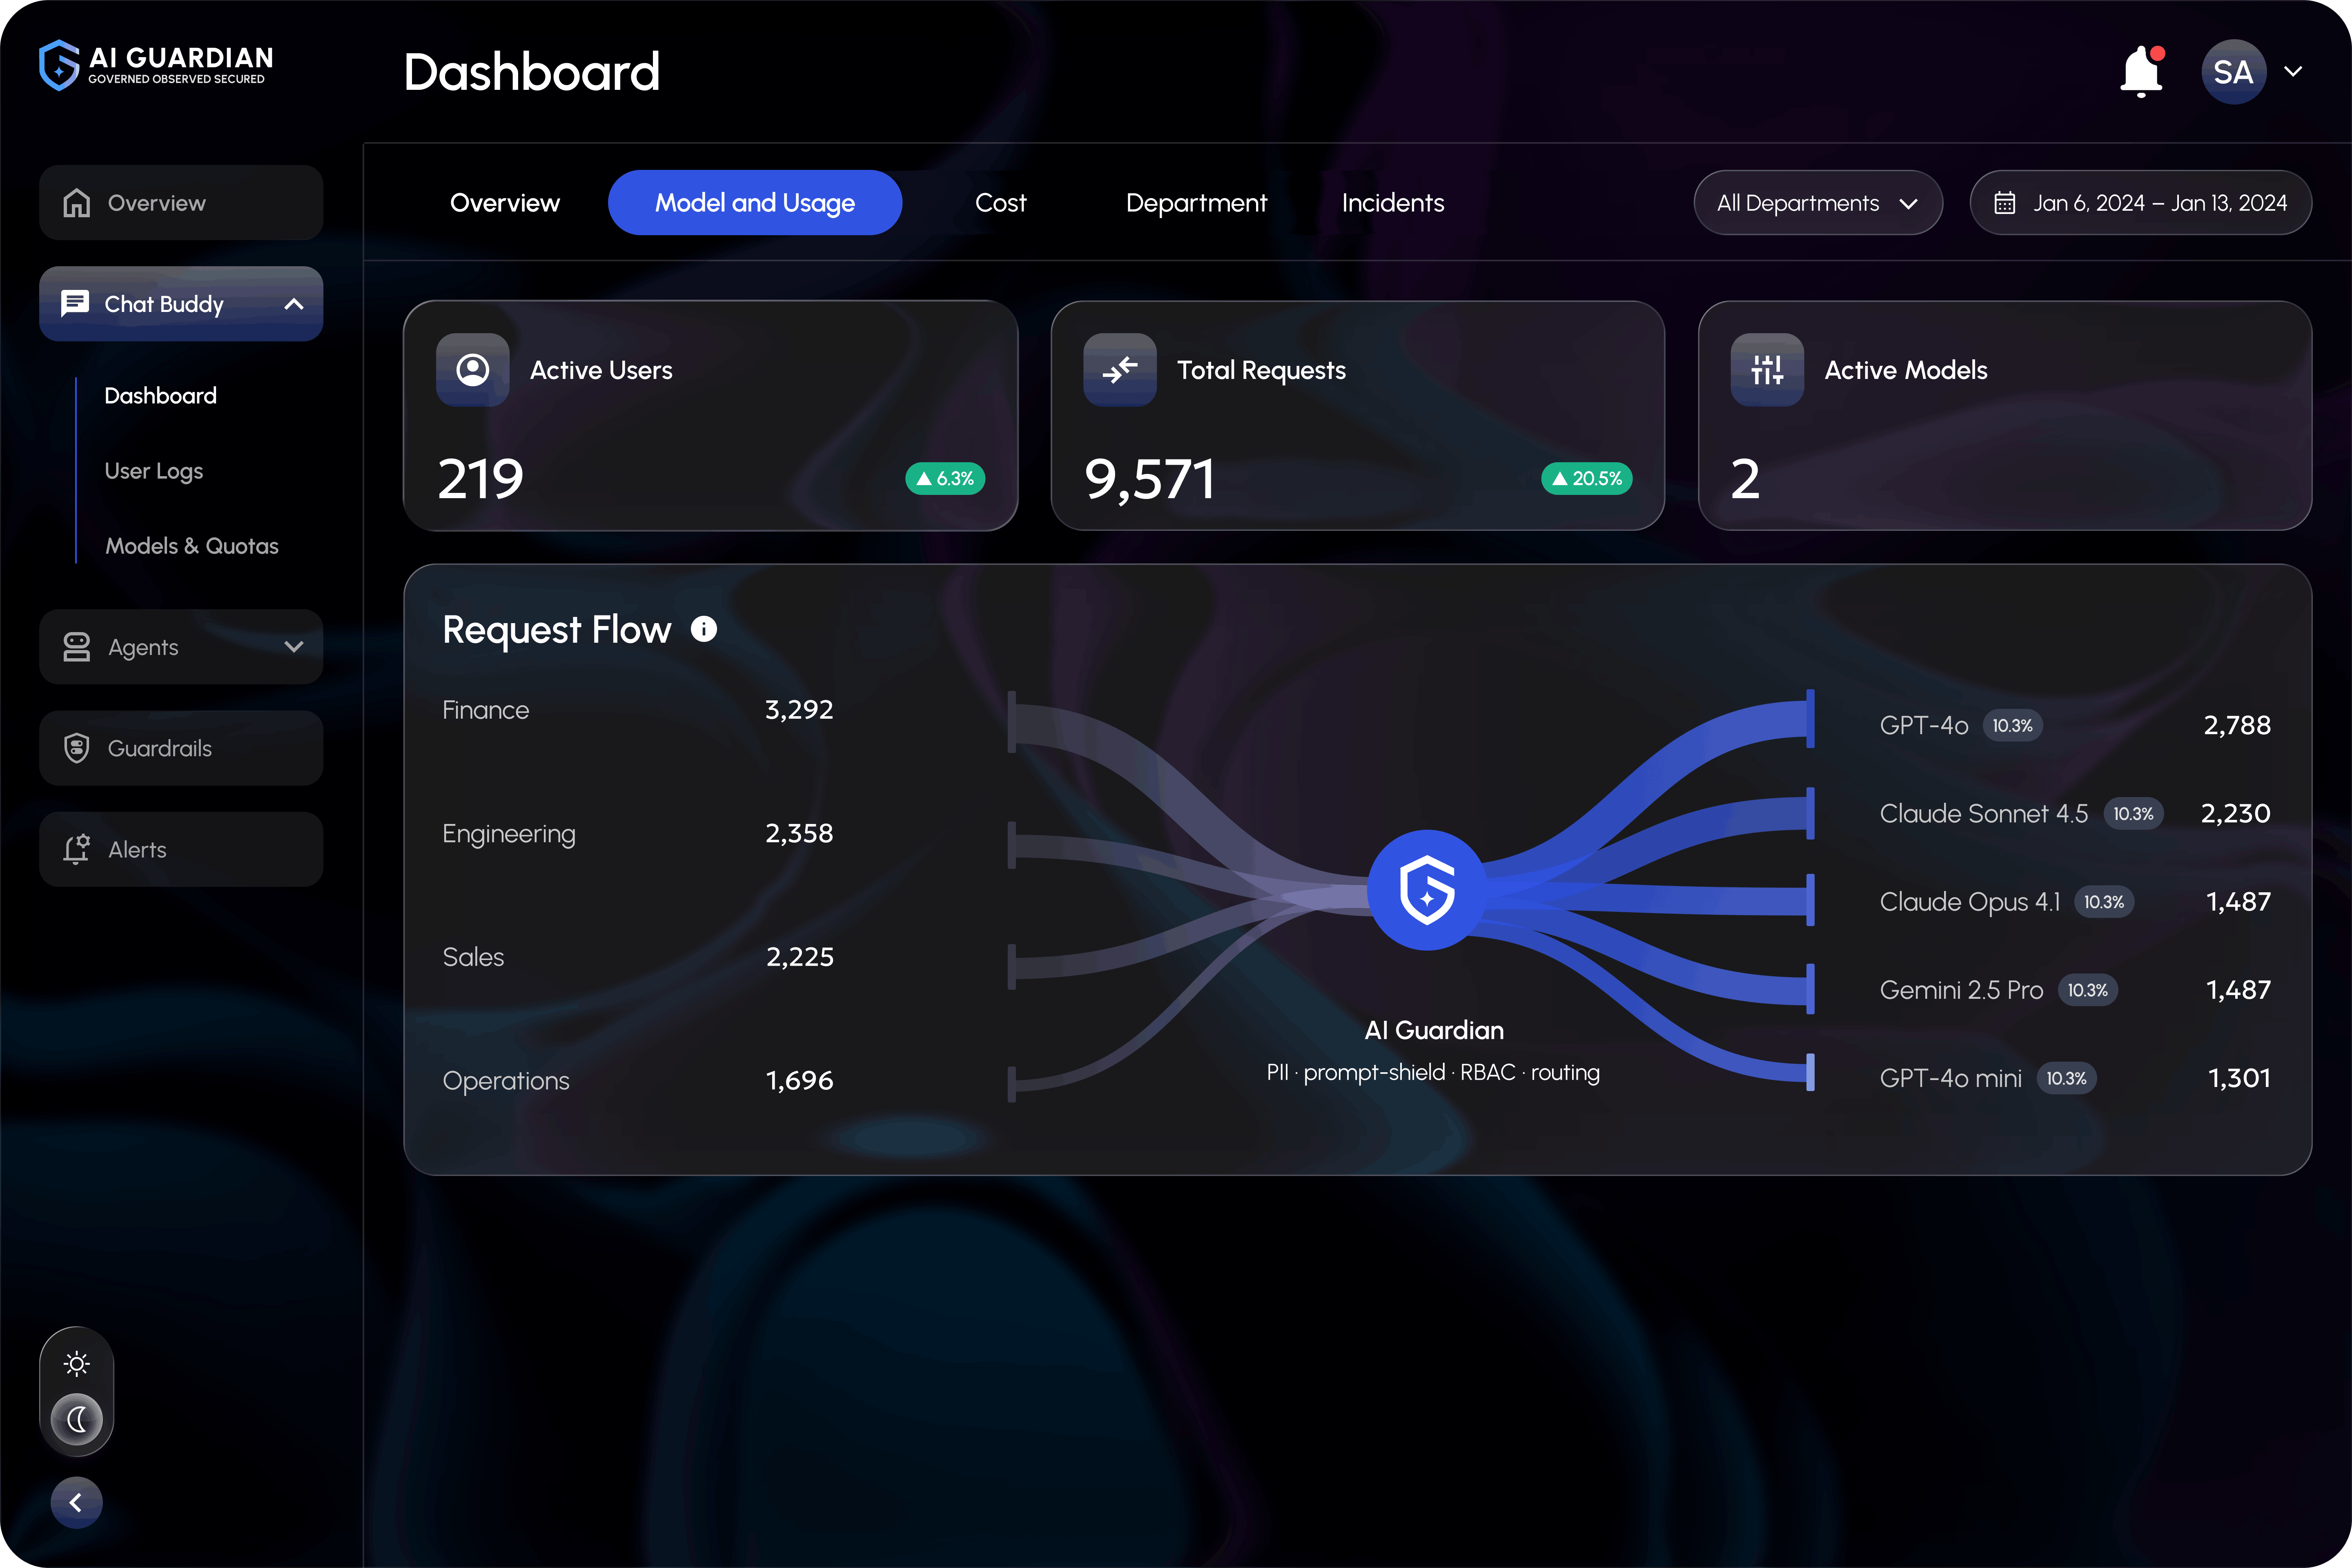
Measured against those six questions, this is what AI Guardian does. It is Folio3's AI governance control plane and sits between people and the models, agents, and data they use, so every request passes the same checks.
IMAGE_URL_HERE in this block's data-image-url attribute with your final image link.
IMAGE_URL_HERE
Identity
SSO maps each user to their role, department, and policy set across Teams, Slack, the web app, and mobile.
Inspection and PII controls
Prompts and attachments are scanned for PII, secrets, and prompt injection attempts. IBANs, national IDs, and financial details are masked before the request reaches any model.
Policy enforcement
Off-domain requests are declined, and content rules are applied consistently across every approved model and agent.
Model routing and spend controls
Requests are routed to the right model based on role, task type, and available quota. Routine work goes to cost-efficient models; complex reasoning gets frontier capacity.
Agent registry
Custom and third-party agents connect through a central registry, inheriting the same identity, redaction, spend, and audit controls as any standard prompt.
Audit and executive visibility
Every response generates a trace covering identity, policy decisions, model used, tokens, and cost. Department heads manage local quotas; risk leaders see org-wide usage and blocked events.
AI Guardian deploys inside the customer's own Azure, AWS, or GCP environment. Prompts and logs stay within the tenant.
AI Guardian governs requests at runtime. It does not replace model-level bias testing or drift monitoring, and it can feed evidence into a program platform if you run one.
One governed path for every interaction
Explore the AI Guardian product page or view the Microsoft Marketplace listing.
How AI Guardian applies this
The table maps AI Guardian's controls to the risk categories above. Where a risk sits outside the request path, it says where extra tooling is needed.
| Risk category | Process step | AI Guardian control |
|---|---|---|
| Shadow AI | Identify | One governed workspace across Teams, Slack, web, and mobile, with SSO enforced for every user. |
| Data privacy exposure | Mitigate | PII and secret redaction applied to prompts and uploaded files before the request reaches any model. |
| Adversarial and agent risk | Mitigate, Monitor | Prompt injection inspection, least-privilege agent access controls and security event logging. |
| Regulatory non-compliance | Assess, Report | Role and department-level policies, off-domain request restrictions and identity-attributed audit traces. |
| Uncontrolled AI spend | Mitigate, Monitor | Role-based model routing, per-department quotas and monthly spend caps. |
| Explainability gaps | Report | Full request traces showing the user, model selected, policy decisions applied, and response generated. |
| Model bias and drift | Monitor | Per-request logs support ongoing review; pair with dedicated MLOps monitoring for training-level bias testing and drift detection. |
Where AI Guardian fits first
Rollouts usually start with the teams where sensitive data already flows through AI and demand for access is highest: banking and financial services, legal and compliance, and procurement. Financial identifiers, contracts, and vendor data carry the most exposure if they reach an unmanaged model. HR, IT, and security follow, where role-based access and usage visibility matter as much as content rules.
How AI Guardian gets implemented
AI Guardian comes with a structured implementation engagement, not just a platform login. After the Phase 1 blueprint is signed off, configuration and deployment take four to five business days, depending on the complexity of the environment.
Phase 1: Requirements and alignment. Working sessions cover existing AI policies, regulatory requirements, and priority use cases. The team defines guardrails, model access permissions, role structures, department quotas, and governance ownership. The output is a documented rollout blueprint signed off before any configuration begins.
Phase 2: Configure, deploy, and go live. Over four to five business days, the platform hierarchy, guardrails, roles, quotas, and dashboards are configured and deployed inside the customer's cloud tenant. Smoke testing runs against real request types before go-live is confirmed.
Ongoing: Monitoring and tuning. Post-launch, policies and model access are adjusted as actual usage patterns emerge. Scheduled reviews keep controls current as new models are adopted and regulatory requirements evolve.
Timelines change with the number of integrations and the target environment.
AI Guardian vs other AI governance approaches
| Factor | Program-layer governance platforms | AI Guardian |
|---|---|---|
| Setup model | Self-serve configuration, often with optional paid services | Implementation included, from requirements through go-live |
| Framework coverage | Pre-built templates for common frameworks | Policies configured to your regulatory mix during alignment |
| Deployment | Varies by vendor: SaaS, private cloud, or on-premises | Runs inside your own Azure, AWS, or GCP tenant |
| Enforcement | Mostly inventory, assessment, and evidence; runtime blocking is often a separate product | Controls on every request: identity, redaction, routing, and spend |
| Not covered | Runtime blocking in many products | Model-level bias testing and drift monitoring |
| Best fit | Teams with dedicated governance staff who prefer self-serve setup | Teams that want runtime controls live quickly and are building governance capacity |
Why teams choose AI Guardian
Built by an AI engineering team: Folio3 was founded by Silicon Valley engineers and entrepreneurs, alums of Intel, Silicon Graphics, and Qualcomm, and graduates of MIT and Caltech. The same team builds production AI for clients. For Opsis Health, Folio3 built a six-agent system that reads meal photos, cross-references live biometric and glucose data, and gives nutrition guidance before the user eats; after launch, the user acquisition rate grew from 5% to 20% (case study). AI Guardian's controls are designed around how models and agents like these behave in production.
Implementation included: The engagement covers requirements, configuration, deployment, and go-live, with scheduled tuning afterward.
Available now: AI Guardian is live at folio3.ai/solutions/ai-guardian and listed on Microsoft Marketplace for Azure customers.
Security credentials, scoped: Folio3 holds ISO 27001 certification, which covers the company's information security management system rather than the AI Guardian product. AI Guardian's SSO, role-based access, in-tenant deployment, and audit logging are architectural controls designed in line with SOC 2 criteria. Folio3 has not undergone a SOC 2 audit.
Expert insight
“Most teams start AI governance by writing a policy, then find out months later that nobody followed it, because the approved tool was slower than the free one on their phone. In every rollout I've managed, the programs that worked started from the other end. They made the governed path the easiest path to use, logged every request from day one, and only then wrote rules based on what people were actually doing. You can't govern AI use you can't see, and you can't see it if people are avoiding you.”
Frequently asked questions
What is AI risk management software?
It is a platform that inventories AI systems, scores their risk, enforces controls, monitors behavior, and produces audit evidence. It should not be confused with software that uses AI to score fraud or credit risk.
How is it different from AI governance software?
The terms overlap heavily. Risk management emphasizes identifying and treating risks, governance adds policy, ownership, and accountability, and most products cover both.
Which frameworks should it support?
At minimum, NIST AI RMF, ISO/IEC 42001, and the EU AI Act. Ask the vendor to show one control mapped to all three.
Does the EU AI Act apply to companies outside the EU?
Yes. It applies to organizations that place AI systems on the EU market or whose AI outputs are used in the EU, wherever they are headquartered.
When do the EU AI Act high-risk rules apply?
Under the 2026 Digital AI Omnibus, stand-alone high-risk systems (Annex III) must comply from 2 December 2027, and AI embedded in regulated products (Annex I) from 2 August 2028. Transparency duties under Article 50 apply from 2 August 2026.
What is shadow AI and why does it matter?
Shadow AI is any AI tool employees use without approval or oversight, such as a personal chatbot account or a free browser extension. It matters because the organization cannot see what data goes into these tools, cannot enforce its policies on them, and has no record to show an auditor. The usual cause is an approved option that is slower or harder to use than the free alternative, so the fix is to make governed AI the easiest route rather than simply banning the rest.
Can a spreadsheet manage AI risk?
For a few AI tools and no regulated data, a written policy and a maintained inventory can hold for a while. Beyond that, evidence assembled by hand is slow and hard to repeat.
Does this software replace bias and drift monitoring?
No. Runtime governance covers how AI is used across requests, while model monitoring covers training-level bias and performance drift, so many programs run both.
Written by the Folio3 AI Editorial Team, with expert input from Muhammad Nasir, Senior Project Manager. Technical content on frameworks, regulation, and AI controls was reviewed by Abdul Sami, Head of AI Development at Folio3 AI, in September 2026.
Final words
AI risk management software closes the gap between how AI is used inside an organization and what that organization can show an auditor or regulator. If most of your AI use is in SaaS tools and you have no central control point, start with inventory, identity, and PII controls, then layer framework mapping on top. If you already run a program platform, add runtime enforcement so its evidence comes from real requests. Either way, ask each vendor to show the six capabilities above on your own use cases before you sign.
Bring your risk categories, frameworks, and cloud environment
Book a demo built around your risk categories, frameworks, and cloud environment, and see redaction, routing, and audit traces on sample requests.

