


On this page
Shadow AI detection software finds the AI tools, accounts, extensions, and agents that employees use without IT approval, and shows what data reaches them. The need is measurable. IBM's 2026 Cost of a Data Breach Report, run with the Ponemon Institute across 602 breached organizations, found that 43% had security incidents involving shadow AI, and that 68% of breached organizations lacked AI governance policies to manage AI or detect shadow AI. This guide covers how detection works, which methods miss which surfaces, what to check before buying, and why detection alone leaves the underlying problem in place.
What is shadow AI detection software?
Shadow AI detection software identifies AI tools, accounts, browser extensions, and agents that employees use without IT approval. It records which users reach them and, in stronger products, what data goes in. The output is an inventory of AI activity that security, compliance, and IT teams can review, approve, restrict, or replace.
Shadow AI itself is any AI use that happens outside the approval, visibility, or policy of the organization: a personal chatbot account used for a work document, a browser extension that summarizes pages, or a team subscription bought on a personal card. A manual audit of SSO logs, expense reports, and surveys catches some of this, but it goes out of date within weeks and cannot see personal accounts, free tiers, or extensions. Software watches continuously and ties each finding to a user.
Detection, governance, and enforcement are different jobs
| Layer | Question it answers | Example |
|---|---|---|
| Detection | What AI is being used? | Find personal AI accounts, extensions, and AI services |
| Governance | What AI use is approved? | Assign tools, owners, roles, and policies |
| Enforcement | What happens to this request? | Mask, block, reroute, or log it before execution |
A discovery product can tell you shadow AI exists. It does not necessarily give employees a safe alternative or enforce policy on the next request.
Why shadow AI slips past IT
IMAGE_URL_HERE in this block's data-image-url attribute with your
final image link.
IMAGE_URL_HERE
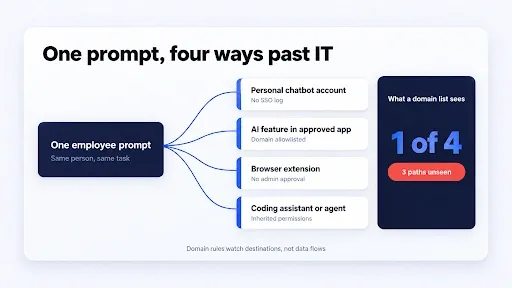
Shadow AI feels like finishing work faster, and it moves through channels that approvals, procurement, and domain lists were never built to watch.
Personal accounts on public chatbots
A personal account signs in with a personal email, so the identity provider never logs it and nobody can enforce retention or training settings. Netskope's 2026 report found 47% of generative AI users use personal accounts, per Vectra AI's summary. The company keeps no record of who used what.
AI features inside approved apps
An approved SaaS product can ship an AI feature in a routine update. The domain stays allowlisted, but data reaches a new processing path, sometimes a new subprocessor. The original security review predates it, and nobody repeats it.
Browser extensions and plugins
An extension can request permission to read and change data on every site the user visits, so a summarizer sees whatever tab is open, including customer records. Extensions install in seconds without an admin and rarely appear in application inventories.
Coding assistants and agents with inherited permissions
Coding assistants read repositories, configuration files, and terminal output, where API keys often sit. Agents run with the launching user's access, so one asked to "clean up the shared drive" reaches everything that user can.
Sensitive data pasted into prompts
The risk sits in the content, not the destination. Rewriting a sentence and summarizing a contract go to the same site, and only one exposes an IBAN. Uploads widen the gap, because a PDF carries every page, not just the paragraph intended.
Unmanaged subscriptions and AI spend
Individual subscriptions land on expense reports and personal cards, often under approval thresholds. Three teams can buy the same tool unknowingly. Finance sees scattered small charges and no view by model or department.
Shadow AI vs shadow IT
Shadow IT moves or stores data in an unapproved application. Shadow AI also processes it in a model, where retention and training terms depend on provider and plan, and employees rarely check which apply. The prompt, not just the app, becomes the unit of risk.
Why domain blocking falls short
Blocking one chatbot domain closes one door. Other tools, embedded features, and mobile data stay open, and a blocked tool can return as a feature inside an allowlisted app. Employees move to tools IT has never heard of, and the signal disappears.
- Data flows matter more than domains. The same domain can carry harmless or sensitive traffic within minutes.
- Prompt content changes the risk. Detection that reads only URLs cannot tell the two apart, so risk scoring needs the content and the user's role.
How shadow AI detection software works
Detection products combine five signal sources. Each sees a different slice of AI activity, so what a method observes explains what a product misses.
Network and DNS traffic analysis
A fast first inventory of which AI services people reach.
- Signals: DNS queries, TLS server names, and API endpoints checked against a list of AI services.
- Gap: Lists lag new tools, and encryption hides the prompt.
Browser and endpoint telemetry
Agents on managed devices report what users actually do.
- Signals: Visited sites, extensions and their permissions, paste and upload events, desktop AI apps.
- Gap: Unmanaged laptops and phones produce nothing.
SaaS and OAuth discovery
Identity provider and SaaS records list AI apps tied to corporate accounts.
- Signals: OAuth grants and scopes, sign-in logs, and app inventories showing AI features in approved apps.
- Gap: A personal-email tool with no corporate grant leaves no record.
Gateway and API inspection
Sits in the request path, so it can act on content before it leaves.
- Signals: Prompt, response, user, role, model, and token count for every routed request.
- Gap: It sees only traffic routed through it.
Data movement and DLP signals
Flags sensitive data heading toward AI destinations.
- Signals: Pattern and classifier matches on files and text, such as card numbers.
- Gap: Free-text prompts often match no pattern.
| Method | What it sees | Blind spots | Best fit |
|---|---|---|---|
| Network and DNS | Traffic to known AI domains and API endpoints from managed networks and devices | Personal devices on mobile data, encrypted content, AI features inside approved domains | A fast first inventory of which AI services are reached |
| Browser and endpoint telemetry | Sites, extensions, paste and upload events, desktop AI apps on managed devices | Unmanaged devices, mobile, server-side agents | Finding extensions and personal-account use on laptops |
| SaaS and OAuth discovery | AI apps connected to corporate identity and data through OAuth grants and SaaS logs | Tools used with personal email and no corporate grant | Auditing connected apps and embedded AI features |
| Gateway and API inspection | Prompt and response content, user, model, and tokens for routed traffic | Anything that bypasses the gateway | Enforcement, per-request evidence, and spend control |
| Data movement and DLP | Sensitive files and known patterns heading toward AI destinations | Free-text prompts and context that patterns do not classify | Protecting defined data classes |
Shadow AI coverage map
No single method covers every surface. The matrix below rates five detection methods against eight places shadow AI appears, based on how each method works. Results in a real deployment depend on configuration and coverage.
- Sees: reliably observes the surface
- Partial: metadata only, or needs extra configuration
- Blind: does not observe the surface
- Sees if routed: visible only when traffic passes through the gateway
The key question is not whether a product "detects shadow AI." It is which surfaces it can observe and which ones remain invisible.
| Where shadow AI appears | Network and DNS | Endpoint and browser | SaaS and OAuth | Gateway and API | DLP |
|---|---|---|---|---|---|
| Personal chatbot on a managed laptop | Sees | Sees | Blind | Blind | Partial |
| Personal phone on mobile data | Blind | Blind | Blind | Blind | Blind |
| AI feature inside an approved app | Partial | Partial | Sees | Blind | Partial |
| Browser extension | Partial | Sees | Partial | Blind | Partial |
| Coding assistant in the IDE | Partial | Sees | Blind | Sees if routed | Partial |
| OAuth-connected AI app | Blind | Blind | Sees | Blind | Blind |
| Agent or MCP server | Partial | Partial | Partial | Sees if routed | Blind |
| API key in code or scripts | Partial | Blind | Blind | Sees if routed | Partial |
Two patterns stand out. Reading across a row, most surfaces need two or three methods working together. Reading the phone row, no method sees it, so the only workable control is an approved path that is easier to use than the personal one.
What DLP, CASB, and secure web gateways miss
Data loss prevention tools classify files and known patterns. Cloud access security brokers track cloud apps by domain, and secure web gateways filter by URL category. Each was built for files, apps, and addresses. A prompt is free text typed into a page that may share a domain with harmless use, so a category or a file pattern often has nothing to classify. These tools remain useful inputs to a detection program. They do not read the request.
Not sure which of these eight surfaces you can see today?
Book an AI Governance Consultation and map your current tools against this matrix before you buy anything.
What to look for in a shadow AI detection tool
Most buyer checklists list features. This one lists checks, each worded as a test a vendor can run on your own use cases during evaluation. Bring a sample prompt containing fake sensitive data.
- AI-specific detection, not SaaS discovery. Ask whether the product recognizes AI endpoints, extensions, and embedded features, or only lists SaaS apps that happen to include AI.
- Real-time visibility into prompts. Scheduled scans miss a paste that takes seconds. Confirm the product sees requests as they happen and can act before data reaches a model.
- Risk scoring per interaction. A visit log is not a risk model. Look for scoring based on data type, role, and destination so responders start with the worst events.
- Identity and role mapping. Activity tied to a device or IP forces manual correlation. Ask for events attributed to a named user, department, and role through SSO.
- Enforcement, not just alerts. An alert after the paste is a record of the leak. Check whether the product masks, blocks, or reroutes at request time.
- Audit-ready evidence trails. Ask for a sample log. It should be structured, identity-attributed, and usable by an auditor without reformatting or manual cross-referencing.
- Private cloud deployment control. Prompts and logs contain your most sensitive text. Confirm whether the product runs in your own tenant or through vendor infrastructure.
- Spend and model visibility. Unmanaged AI subscriptions hide in expense reports and personal cards. Look for cost attribution by model and department, plus quotas that hold.
These eight checks describe a control point, not a report. Products that pass all eight sit in the request path.
Ready to test a vendor against these eight checks?
See the checks applied to a live AI Guardian request.
Why detection alone is not enough
Finding shadow AI is the first half of the job. The second half is deciding what employees do instead, because every finding that ends in a block or a warning leaves the original need unmet.
Bans push usage underground
A ban removes visibility faster than it removes usage. Employees who were using a tool openly switch to personal devices or to tools nobody has heard of, and the detection program loses the signal it just built.
Alerts without an approved alternative
An alert tells the security team about a paste. It gives the employee nothing to do next. Without a sanctioned tool that handles the same task, the same paste happens tomorrow and the alert queue grows.
Monitoring erodes employee trust
Some detection products are built on screen recording and keystroke capture. They answer what happened, and they also tell employees their whole workday is watched. A request-level log tied to identity records the AI interaction itself.
| Question | Activity monitoring | Governed path |
|---|---|---|
| What is recorded | Screens, keystrokes, and app and site use, depending on the product | User, model, policy decision, tokens, and cost for each AI request |
| What happens to a risky prompt | Varies by product. Ask whether it acts before data leaves | Sensitive data is masked and off-domain requests are declined before the request reaches a model |
| What employees experience | A monitored workday | An approved workspace with sanctioned models |
Detect, replace, then govern
The order matters. Detection produces the inventory. A governed replacement gives people an approved place to move that usage. Governance then tightens rules using real request data. IBM's 2026 report found that among organizations that experienced an AI-related breach, 92% lacked proper AI access controls such as role-based access policies and multifactor authentication. Discovery identifies unauthorized use. Access controls and a governed path reduce the exposure after it is found.
From shadow AI detection to a governed AI path
Detection tells you where unmanaged AI use exists. AI Guardian addresses what comes next: giving employees an approved path where identity, sensitive-data controls, model access, spend, and audit evidence can be enforced on each request.
AI Guardian is not a replacement for network, endpoint, or SaaS-discovery controls used to find AI activity outside its path. It complements them by providing the governed environment that discovered usage can move into.
The same prompt, two paths
A procurement analyst pastes a vendor agreement that contains bank details into an AI tool to check it against internal policy. The task is identical. The path decides what the company can see and control.
| Step | Personal chatbot account | AI Guardian |
|---|---|---|
| Where the request starts | A personal account in a browser tab | Microsoft Teams, Slack, the web app, or mobile, with SSO |
| What leaves | The full text, including account numbers | Bank details and other identifiers are masked before the request reaches a model |
| Which model answers | Whatever the account offers | The approved model for that user's role, within department quota |
| Who acted | Not attributed to a user, role, or policy | Identity, role, and policy set matched before the request runs |
| What is on record | Nothing the company can audit | A trace of identity, policy decisions, model, tokens, and cost |
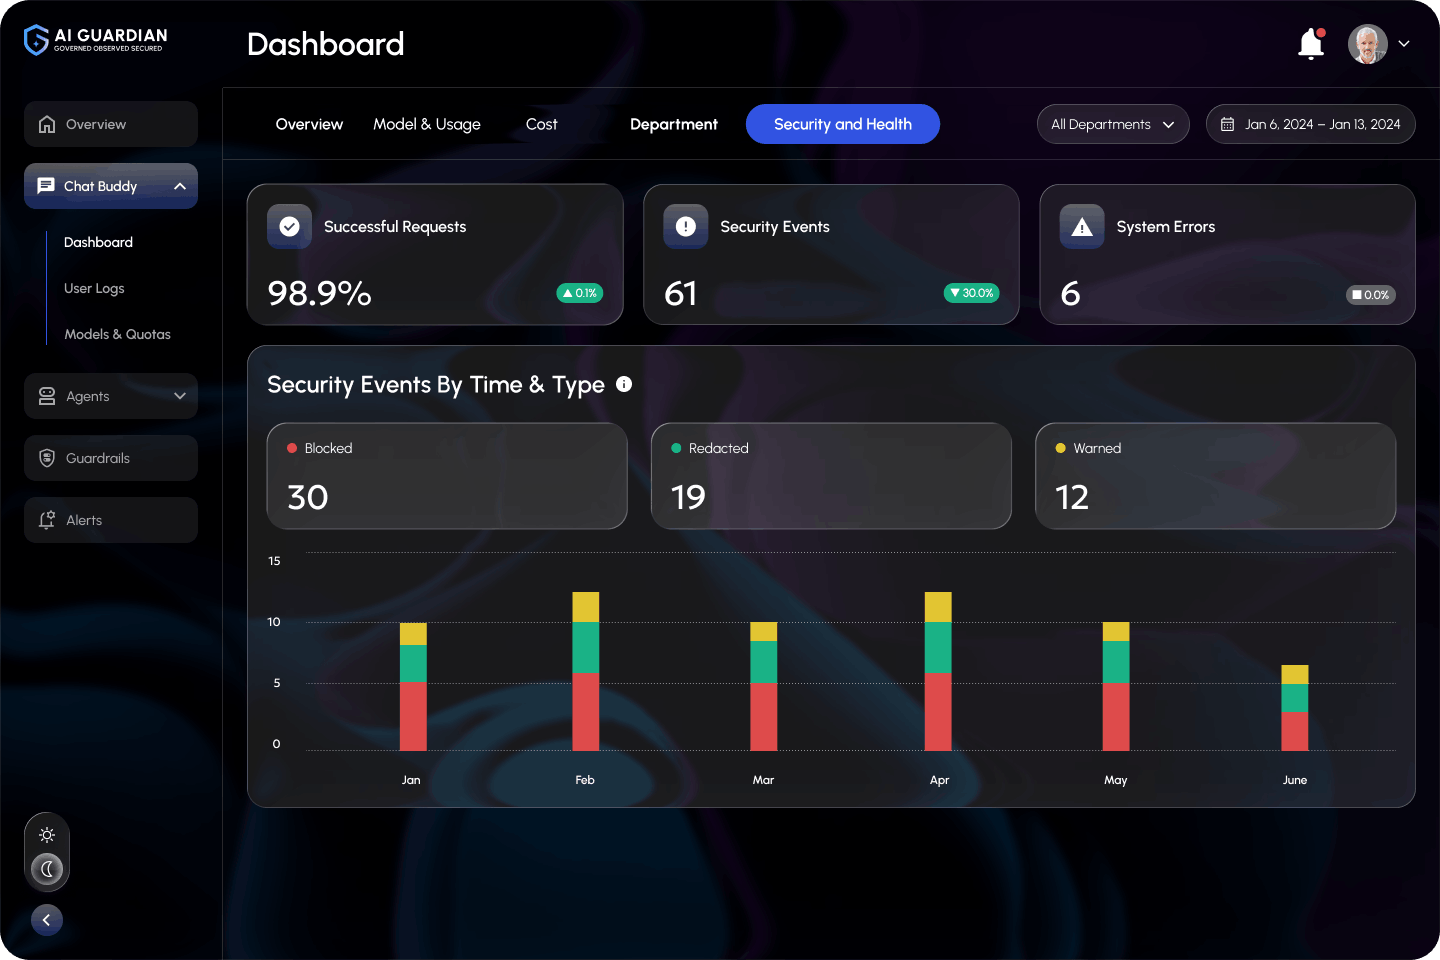
How AI Guardian handles every request
IMAGE_URL_HERE in this block's data-image-url attribute with your
final image link.
IMAGE_URL_HERE
- Step 01: Identity. SSO matches the user to a role, department, and policy set.
- Step 02: Inspection. Prompts and files are scanned for PII, secrets, and prompt injection attempts before any external model sees them.
- Step 03: Routing. Policy checks departmental quotas, permissions, and model access, then routes to the approved model for that role and task.
- Step 04: Orchestration. Governed agents retrieve company knowledge and run approved actions while inheriting the same identity and security controls.
- Step 05: Audit. The response returns while token usage, cost, policy decisions, model activity, and the identity-attributed trace are logged.
Want to see a request move through all five steps?
Book a walkthrough built around your roles, data types, and cloud tenant.
Shadow AI detection capabilities
- Identity-attributed activity logs. Every request carries the user, role, department, model, tokens, cost, and policy decision, so audit questions get answers without log reconstruction.
- PII, secrets, and injection scanning. Prompts and files are scanned for personal data, secrets, and prompt injection attempts before any request reaches an external model.
- Multi-page document redaction. IBANs, national IDs, phone numbers, and financial details are masked across multi-page attachments, with sanitized previews shown before anything is transmitted.
- Role-based model access. SSO maps each user to a role and policy set, so each role reaches only the approved models that its work requires.
- Off-domain request blocking. Requests unrelated to business tasks are declined, which keeps organization-funded AI capacity aligned to approved use cases.
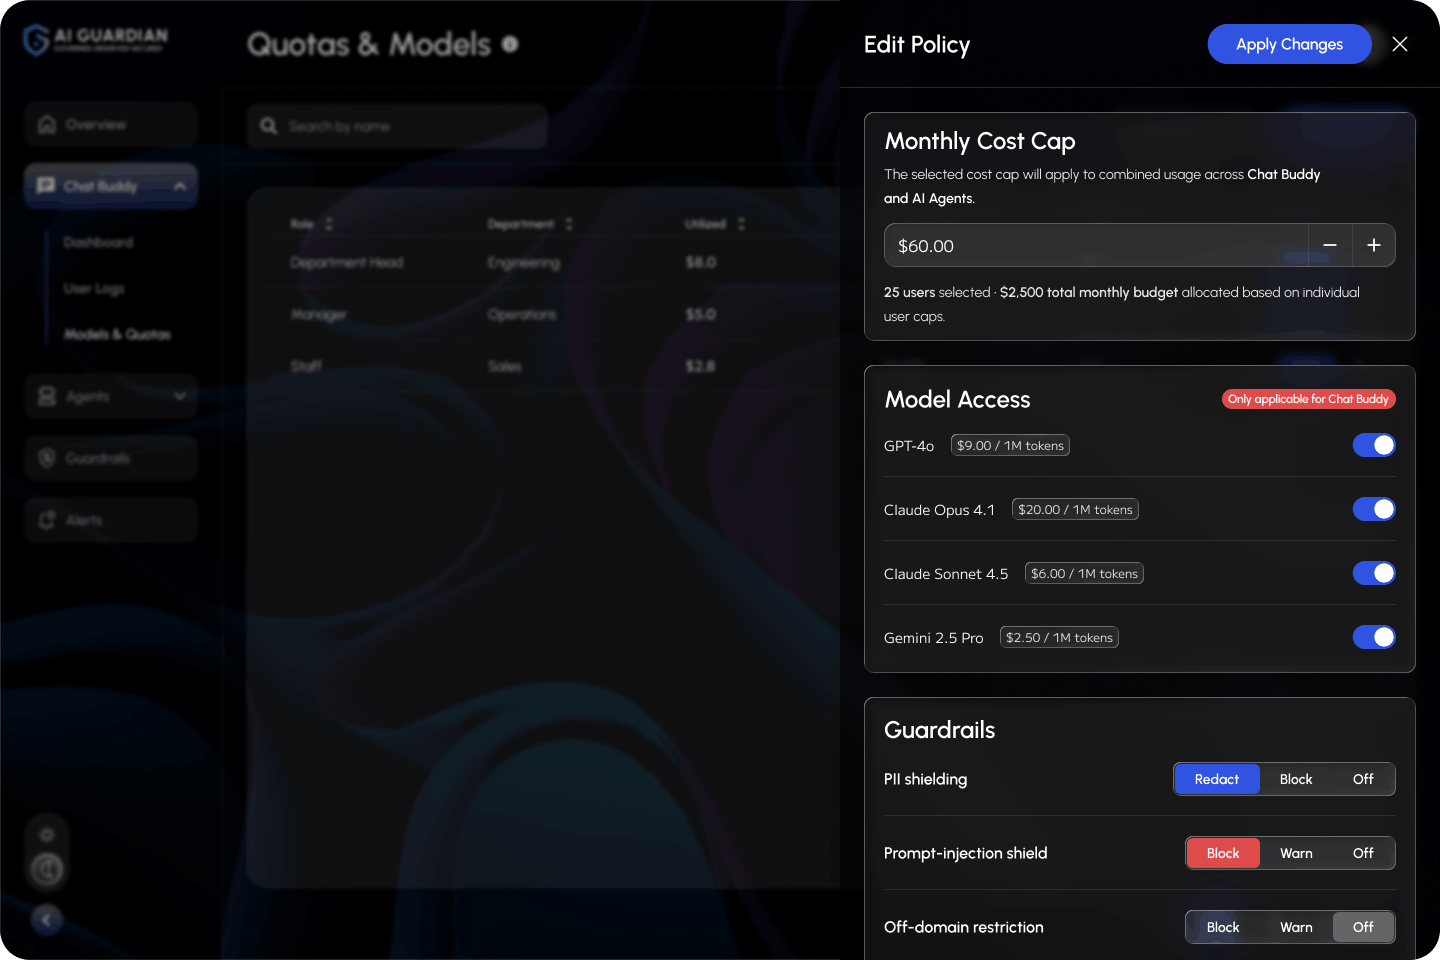
- Spend caps and token quotas. Monthly caps and token quotas apply by department or user role, and cost traces are recorded for each request.
- Agent registry governance. Custom and third-party agents connect through a central registry and inherit the same identity, redaction, spend, and audit controls as any prompt.
- Department and executive dashboards. Department heads manage local quotas and model access, while risk leaders see organization-wide spend, blocked events, and identity-attributed audit history.
What AI Guardian covers, and what it pairs with
AI Guardian governs every request that runs through its control plane, across Teams, Slack, the web app, and mobile. It does not observe a personal account on a private phone or a tool that never touches the governed path. Teams that also need to find tools running outside that path can pair AI Guardian with network or endpoint controls. The governed path then gives employees an approved place to move that usage.
Stop paying for shadow AI sprawl
IMAGE_URL_HERE in this block's data-image-url attribute with your
final image link.
IMAGE_URL_HERE
- Route routine work to cheaper models. Extraction, classification, and simple questions go to cost-efficient models, while complex reasoning uses frontier capacity.
- Set department spend caps. Monthly dollar caps and token quotas apply by department or role, so premium model capacity stays with the work that needs it.
- See cost per request. Cost and token traces attach to each request, which replaces scattered invoices with attributable usage.
- Model the savings before committing. AI Guardian's modeled mixed-workload scenario shows an overall opportunity of ≈30% lower AI spend.
The ≈30% figure is an AI Guardian modeled scenario, not a benchmark or guaranteed saving. Actual results depend on workload complexity, model mix, token usage, pricing, routing rules, and user behavior.
Who owns shadow AI risk
| Owner | What they need | What AI Guardian provides |
|---|---|---|
| CISO and compliance | Audit evidence for every AI request | Identity-attributed traces covering policy decisions, model, tokens, and cost |
| CIO, CTO, and CFO | Spend visibility across models and departments | Quotas, spend caps, and cost traces by request |
| Line-of-business leads | Local control without engineering tickets | Department dashboards for quotas, model availability, and active users |
| Platform teams | Policy and integration ownership | Role and guardrail configuration, and a central agent registry |
See these controls applied to your roles, your data types, and your cloud tenant.
From requirements to go-live in days
Rollout runs in two phases. Alignment sessions define policies, roles, and quotas, and configuration, deployment, and go-live follow once the rollout blueprint is approved. Timing depends on business units, policies, integrations, and security requirements.
- Requirements and alignment: Two-to-four-hour sessions review AI policies, regulatory requirements, hierarchy, and priority use cases. The output is an approved rollout blueprint.
- Policy and guardrail mapping: Guardrails, model access, permissions, and approval boundaries are defined against your policies and roles.
- Configure roles, budgets, and quotas: The platform hierarchy, roles, budgets, quotas, dashboards, and administrator views are configured to the blueprint.
- Deploy inside your tenant: AI Guardian is deployed in your cloud environment, and connectivity and configuration are validated.
- Smoke test and go live: Smoke testing runs before go-live, and operational controls are handed over. Steps two through five take four to five business days.
What AI Guardian costs, and why teams trust it
Pricing has two parts: a one-time implementation and a quarterly platform license. Final terms depend on scope, organizational complexity, integrations, and deployment requirements. Proof points below are capability facts, not client case studies.
- Implementation from $15K, one-time. Covers requirements collection through go-live in your environment.
- Platform license from $8K per quarter. Ongoing quarterly licensing after implementation and launch.
- 20+ years of engineering and 950+ projects delivered. Folio3 builds enterprise solutions and governs AI with the same engineering team.
- ISO 27001 certification. The certification covers Folio3's information security management system, not the AI Guardian product.
- Microsoft Marketplace listing. AI Guardian is available through Microsoft Marketplace for Azure customers.
“Teams read shadow AI findings as a list of people who broke the rules. I read them as a map of where the approved tools failed the job. When the same unapproved tool shows up in three departments, that is a requirement nobody wrote down. The teams that handle this well approve a governed version of what people already use, then tighten the rules once every request is tied to a person and a role.”
Bring shadow AI into a platform you can defend
Employees will use AI either way. Give them an approved path with identity-attributed evidence for every request.
Give shadow AI an approved path
Book a consultation or a demo built around your roles, data types, and cloud tenant.
Frequently asked questions
What is shadow AI detection software?
It is software that finds AI tools, accounts, extensions, and agents used without IT approval, and shows which users and data are involved. Stronger products also score risk and act on requests as they happen.
How do you detect shadow AI in an organization?
Combine network and DNS analysis, browser and endpoint telemetry, SaaS and OAuth discovery, and gateway inspection, because each method misses surfaces the others see. Then tie every finding to a user and role so it can be reviewed.
What is the difference between shadow AI and shadow IT?
Shadow IT stores or moves data through unapproved apps, while shadow AI also processes that data in models whose retention and training terms depend on the provider and plan. That makes the prompt content, not only the app, the unit of risk.
Can DLP or CASB tools detect shadow AI alone?
Usually not. They classify files, patterns, and domains, and prompts typed into a chat box, browser extensions, and embedded AI features often fall outside what they were built to inspect.
Do shadow AI detection tools read prompts?
Some do and some only log domains, and that difference decides whether risk can be scored per interaction. Any product that reads prompts should run in your own cloud tenant so prompt text stays in your environment.
Does blocking ChatGPT stop shadow AI?
No. It closes one domain while other tools, mobile data, and embedded features stay open, and it removes visibility into where usage moves next.
What is the best shadow AI detection tool?
The best fit depends on which surfaces you need to see and whether you need enforcement or only reporting. Test each product against the eight checks above using your own sample prompts.
How long does AI Guardian take to deploy?
Requirements sessions run two to four hours, then configuration, deployment, and go-live take four to five business days once the blueprint is approved. Timing varies with business units, policies, integrations, and security requirements.
Can AI Guardian run in our private cloud?
Yes. It deploys inside your own cloud tenant, such as Azure or AWS, so prompts and logs stay within your environment.
Do I need employee monitoring to control shadow AI?
No. A governed path logs each AI request by user, model, policy decision, tokens, and cost, which gives auditors evidence without watching the whole workday.
What are examples of shadow AI?
Examples include a marketer summarizing a customer list in a personal chatbot account, a developer using an unapproved coding assistant, a summarizer extension reading open tabs, and a team paying for an AI subscription on a personal card. Each stays invisible to procurement for a different reason.
Is shadow AI a compliance risk?
Yes. Personal data pasted into an unapproved tool can conflict with privacy rules such as GDPR data minimization, and the company has no log to show a regulator what was shared. Regulated data such as health or payment records raises the stakes because nobody reviewed the tool's retention terms.
Written by the Folio3 AI Editorial Team, with expert input from Muhammad Nasir, Senior Project Manager. Technical content reviewed by Abdul Sami, Head of AI Development at Folio3 AI, in September 2026.

